What Refrigerator Hacks Reveal About ICS Exposure
Waves of cyberattacks on refrigerators across Europe remind us that OT and ICS remain perpetually exposed. Here are a four reasons why.
Waves of cyberattacks on refrigerators across Europe remind us that OT and ICS remain perpetually exposed. Here are a four reasons why.
Censys detects 1,465 hosts running exposed instances of ARTEX, an open-source, LLM-driven autonomous pentesting framework that has been linked to malicious activity from multiple threat groups.
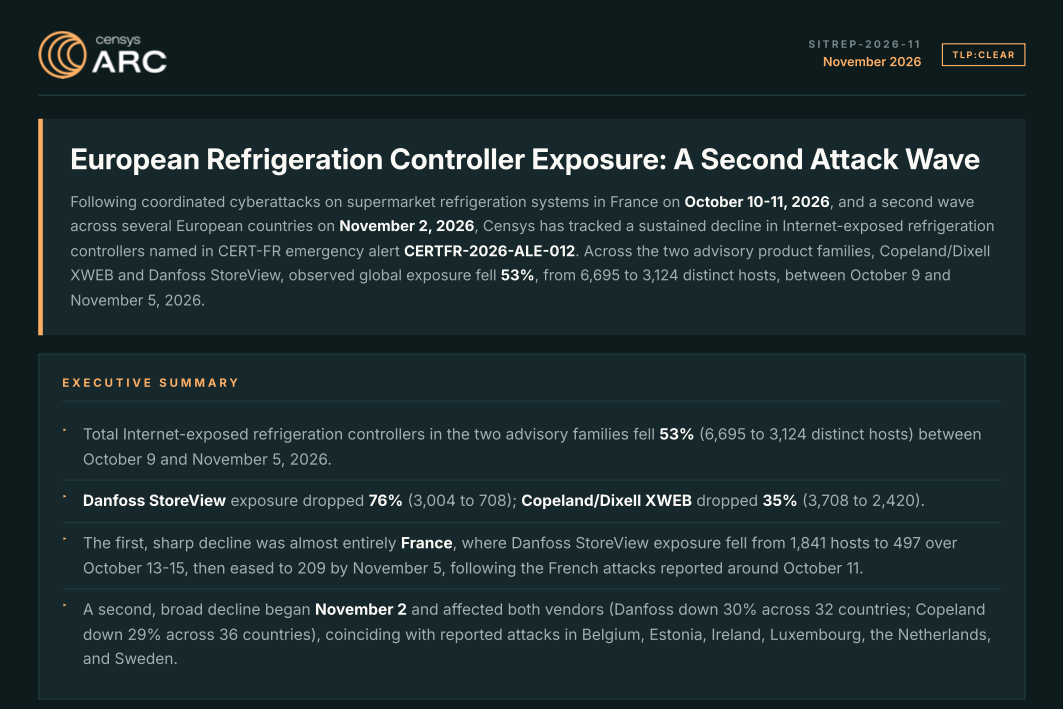
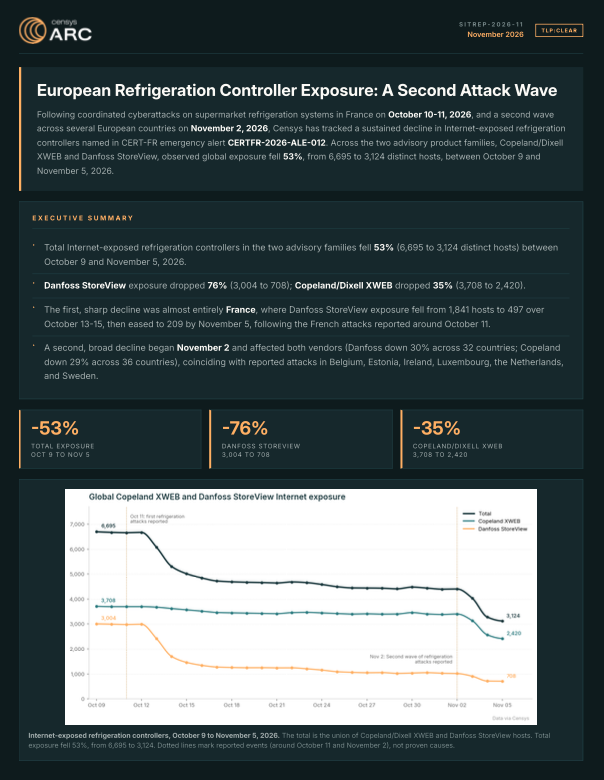
Censys tracks a decline in Internet exposed refrigerator controllers named in CERT-FR emergency alert CERTFR-2026-ALE-012. Learn more.
In the early hours of Monday, November 2, stores in at least seven major supermarket chains, butchers, and small grocers across Europe suffered cyber attacks targeting their commercial refrigeration controllers, mirroring similar incidents observed in France three weeks ago. This time, grocers in Belgium, Estonia, Ireland, Luxembourg, The Netherlands, and Sweden have […]
After "Black October," ARC researcher Himaja Motheram reflects on how well we're protecting aging software in the face of emerging AI threats.
Censys Starter is now a subscription with flat one-credit-per-action pricing and five free searches a day for every user.
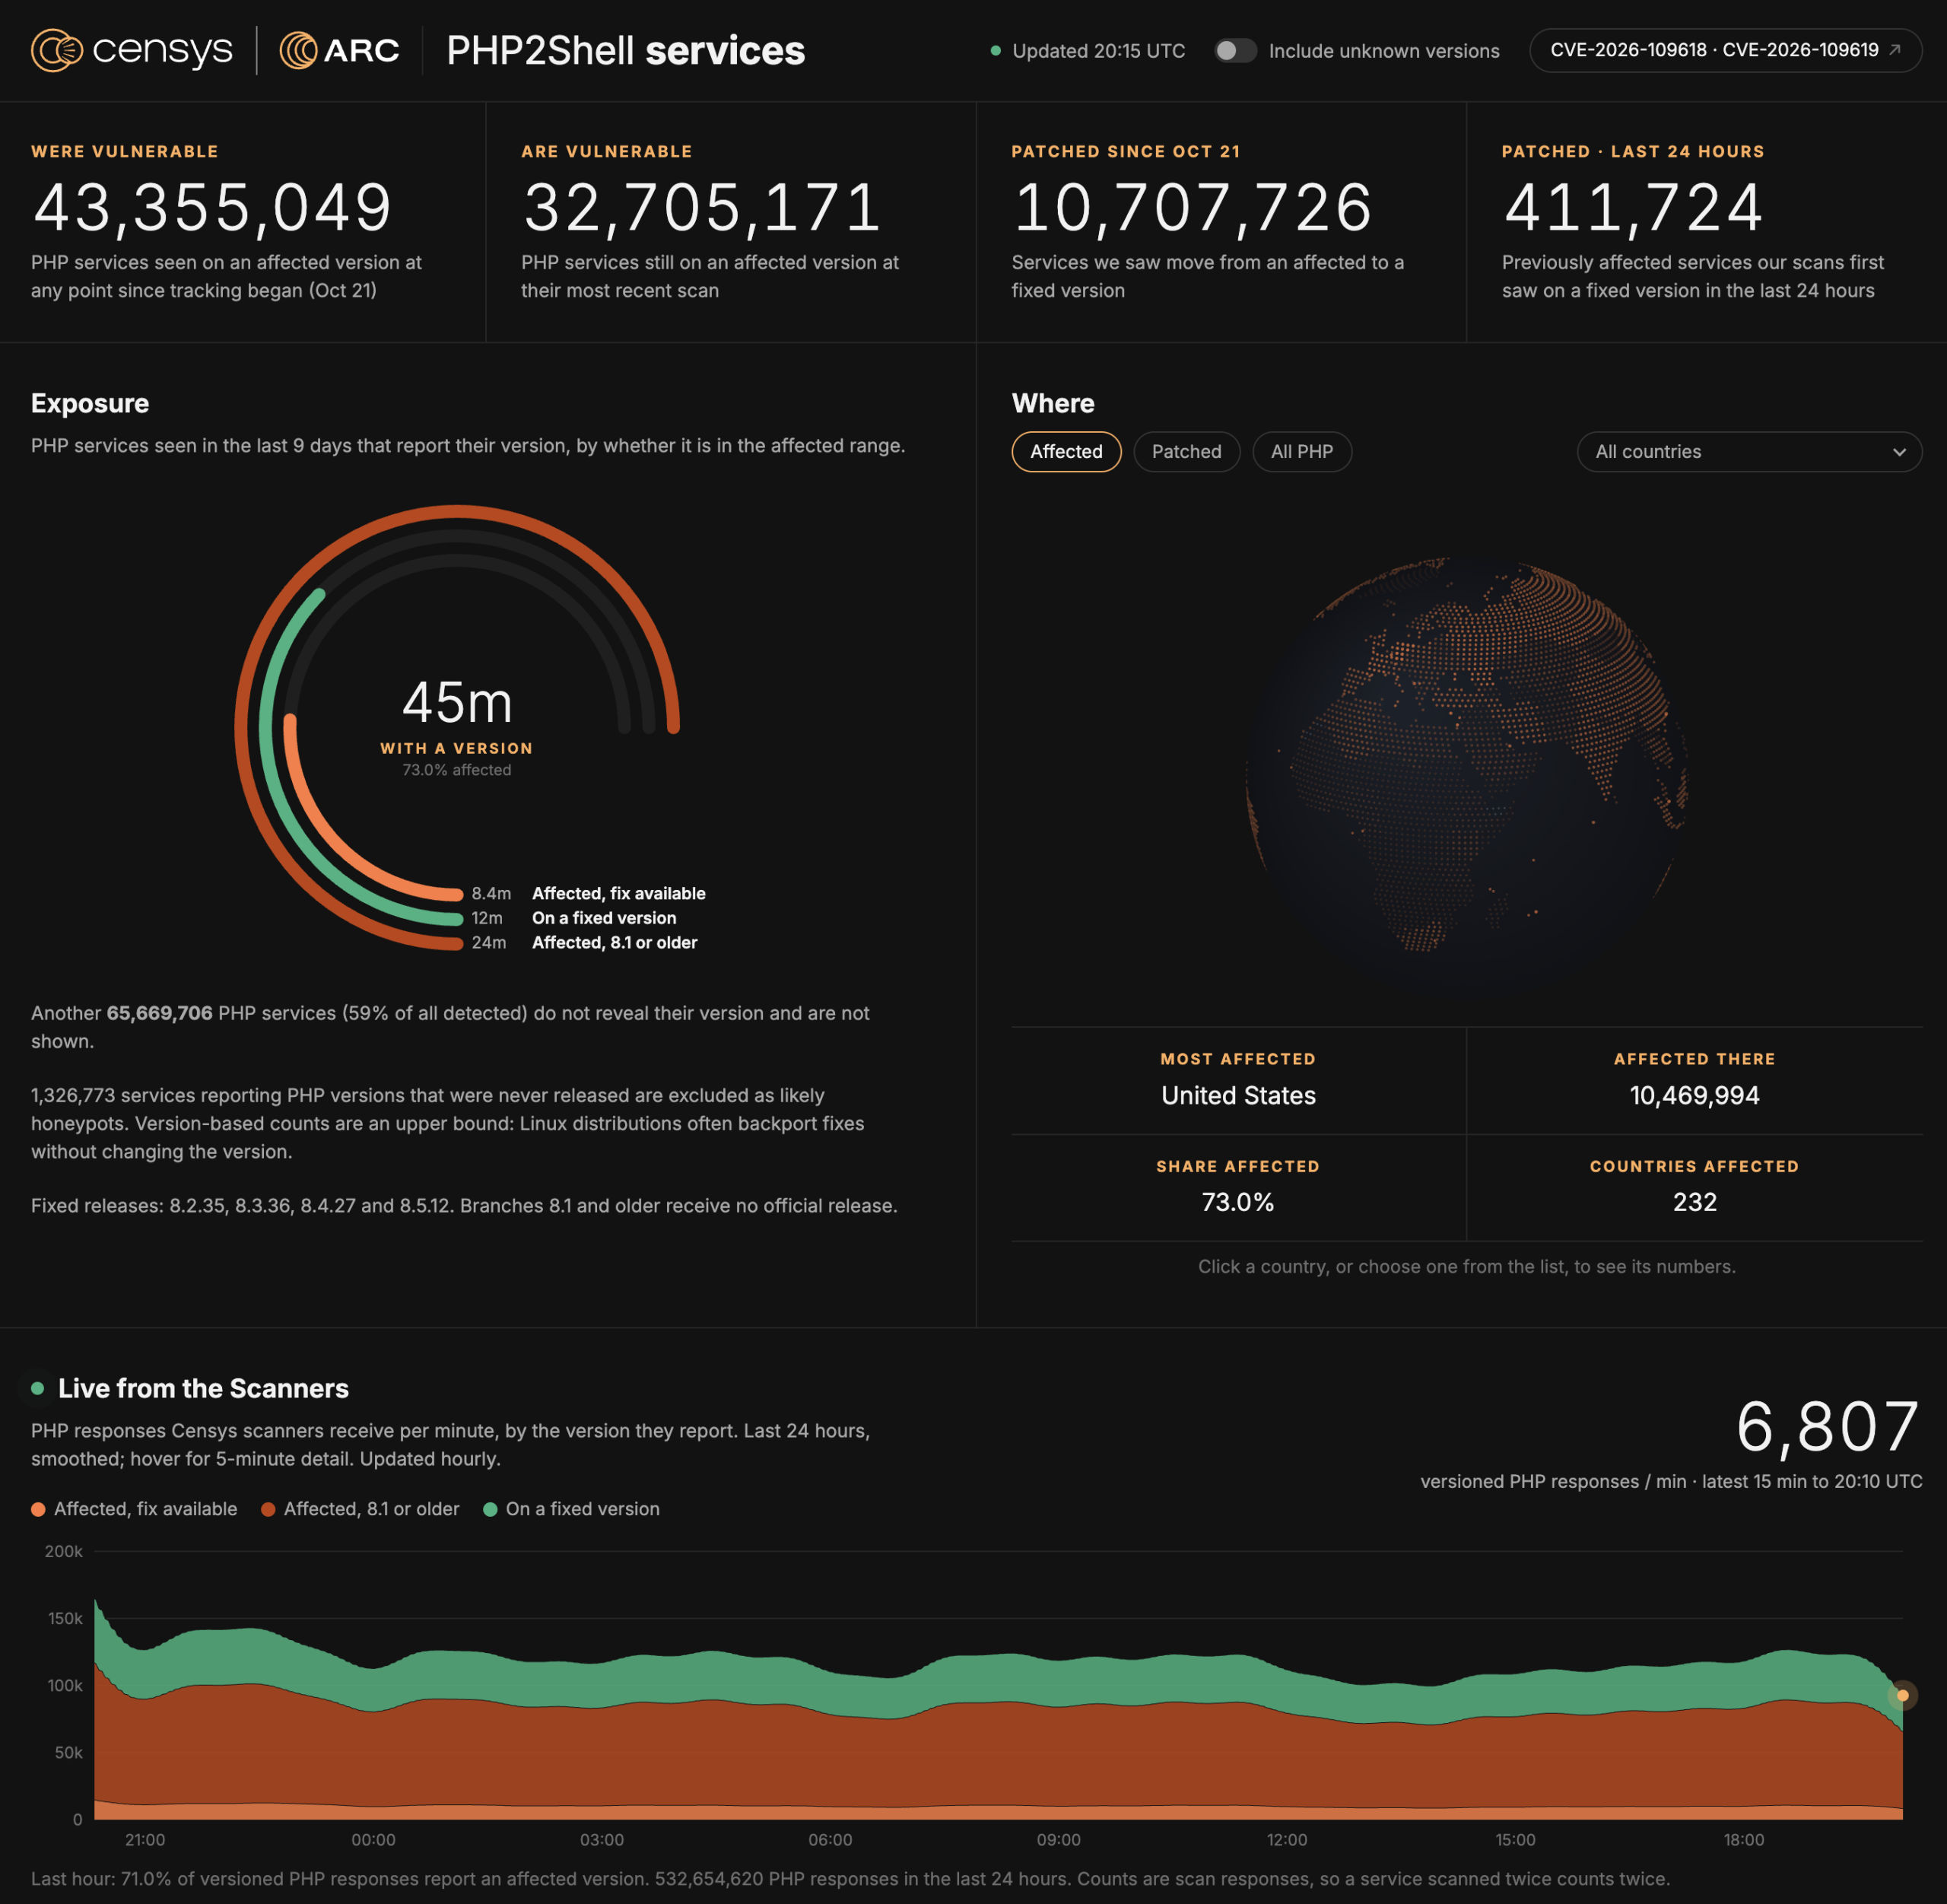
Get details of how PHP2Shell unfolded, why counts differ, and how Censys builds its map of Internet threats and vulnerabilities.
Learn how Censys Investigator works, example use cases, and how you can use it to build repeatable workflows in your environment.
See what’s really running on your website. Censys ASM’s web scanning surfaces hidden risks across your attack surface, automatically.
A review of the attacks targeting refrigerators in France via Danfoss controllers, resulting in spoiled food and, in some cases, fires.
New research from Censys’ 2026 State of the Internet Report challenges familiar assumptions about the Internet and its threats.
Detect typosquatting, phishing domains, and fake logins. A hands-on Censys guide to brand protection, fraud prevention, and takedowns.
CISA-flagged Cisco SD-WAN flaws, ransomware-linked STOMP brokers, and exposed Hikvision cameras: see what scanners we added this month.
Key judgments Background: DarkSword and Coruna DarkSword is an exploit chain for iOS that Google Threat Intelligence Group (GTIG) first documented publicly in March 2026. The chain attacks WebKit and JavaScriptCore to gain code execution, escapes the browser sandbox, escalates to kernel privileges, and injects into SpringBoard, the iOS process that manages app […]
At 2 a.m., a workstation makes an outbound TLS connection to a VPS on port 7443. The EDR flags it. A Tier 1 analyst on her third night shift (and her third cup of coffee) pulls up the IP: DigitalOcean, Linux, a self-signed certificate, nothing in the usual reputation feeds. She writes “no further action” […]
Censys tracks 131 hosts exposing Mythic to the public Internet. Learn about the C2 framework and how to defend against it.
Censys analyzes vibe-coded AI apps that target students and children. Unprotected and not yet detectable with conventional threat detection.
CISA-flagged KNX systems, exposed Redshift clusters, and camera botnets: See what scanners we’ve added this month and how to check your exposure.
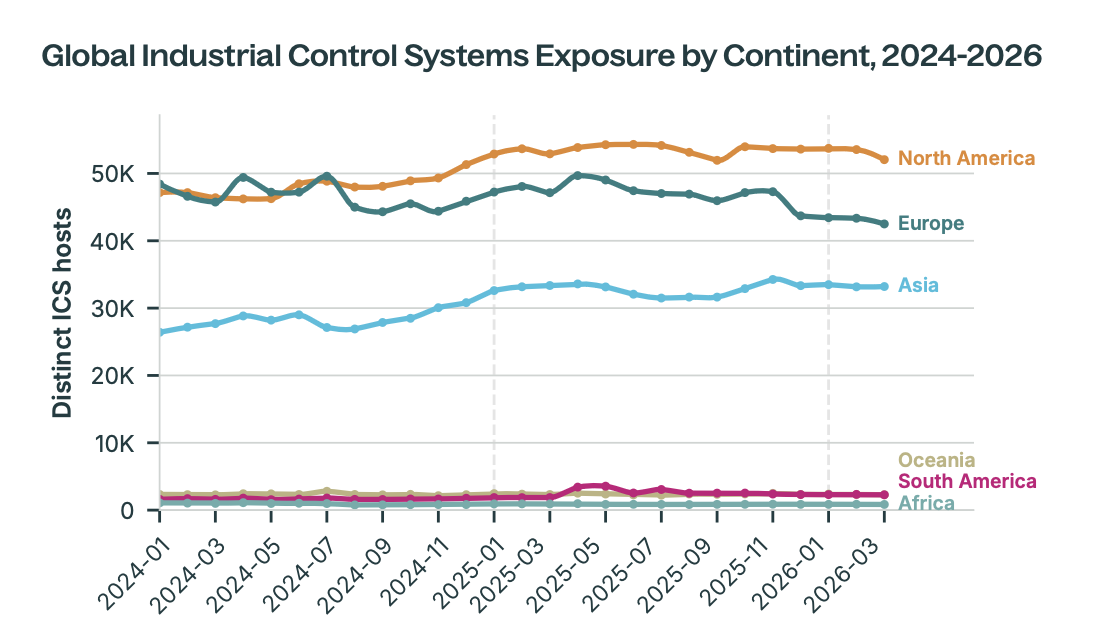
New data from Censys' upcoming State of the Internet Report reveals a major blind spot in Internet-exposed industrial control systems (ICS).
Most deployments of the NPS tunneling tool are benign. Some are not. Censys ARC shares signals for distinguishing the benign from the malicious.