Censys To Unveil Attack Surface Visibility Platform at Black Hat

    New Enterprise Offering will Provide Automatic Attack Surface Monitoring and Real-time Alerts to Protect Against Attackers and Data Breaches LAS VEGAS — Censys, Inc., the leading provider of Internet security data trusted by the likes of Google and The US Department of Homeland Security, today from Black Hat USA 2019, announced the upcoming launch of its […]
    New MySQL-Related Default Insecurity Affects 7500+ Apps

    Posted on August 21st, 2019 Allows for Authentication Bypass & Data Leaks This week, an anonymous researcher discovered and reported an issue with the SphinxSearch application used with MySQL databases: “TL;DR: SphinxSearch comes with a insecure default configuration that opens a listener on port 9306. No auth required. Connections using a mysql client are possible.” […]

    New! Search Censys for Prometheus Endpoints

    We’ve recently added a new protocol to our IPv4 data sets that lets you easily search for exposed Prometheus endpoints. Since these applications can lead to data loss if not properly secured, it’s important to find any that are still are the Internet that you and your team are no longer using so you’re not […]

    New Protocol: Find Exposed Kubernetes Components

    Posted on August 13th, 2019 Kubernetes (sometimes shortened to K8s) is an open-source container-orchestration system released in 2015 that’s commonly used for automating application deployment, scaling, and management. Kubernetes use is growing in popularity because it saves engineering teams time and work at scale. Since the technology is fairly new and the adoption is so […]

    Announcing Our Attack Surface Management Platform

    We’re excited to announce that our new enterprise security platform is in limited, closed beta! We plan to make Censys Platform, our first SaaS product, available to everyone in Fall 2019. Today, we’re working with beta customers to create an automated, streamlined way for businesses to get global visibility about their attack surfaces. We’ve heard […]

    Around 9700 Microsoft Exchange Servers Affected by Privilege Escalation Vulnerability

    A new CVE was reported (CVE-2019-1136) that allows for an attacker to access email mailboxes of any user, if exploited. Now, no known exploits for this exist yet, but any vulnerability that allows for privilege escalation attacks warrants the attention of IT and security teams. Microsoft posted about this vulnerability recently and they had this […]

    Discover Your Potentially Vulnerable SMB Servers

    The Microsoft Server Message Block (SMB) protocol is mostly used for local network file sharing and access to remote services in many businesses who use Windows PCs in their environment. SMB is also a really good example of low-hanging fruit for attackers, because it’s a protocol used across many services and has a lengthy history of […]

    Around 1600 Sharepoint Servers Vulnerable to Attack

    Update May 22, 2019 This is an enterprise only search, but querying Censys raw data, we find Sharepoint running on non-standard ports. We analyzed the raw server headers that we collect on our 1000 ports data and searched for the vulnerable version strings, and also the service name Microsoftsharepointteamservices. By including our 1000 port banner data in our […]

    Prevent Unnecessary Risk from pcAnywhere

    Posted on May 21st, 2019 Originally released for Windows back in 1993, Symantec’s pcAnywhere enabled the user to access a host computer running pcAnywhere remotely. The concept of remote access makes sense from a usability standpoint, but it presents additional security challenges that we must contend with. Similar to the issues we reported with the remote […]

    How to Make Sure Your Elasticsearch Databases Aren’t Exposed

    Most organizations that use Elasticsearch databases use it to store business and customer information. It’s popular for web applications because it allows for easy ingestion and search, making powerful applications easy to develop. Since they often contain a wealth of sensitive data, its critical that those servers be appropriately protected to prevent data leaks. In […]

    Hunting for Threats: Coinhive Cryptocurrency Miner

    In this article, we’ll teach you how to think like threat hunters and use the open source tool YARA alongside Censys to find Coinhive, a cryptocurrency miner service. Created to help security analysts, YARA (now managed by VirusTotal) allows users to write complex rules/descriptions to identify and classify malware. Yara is flexible enough to let you iterate over HTML […]

    Update ASAP: Apache HTTP Web Server Patch Fixes Critical Security Issue

    Apache HTTP Web Server users should update their servers immediately to prevent critical security flaws for cloud and shared web hosting providers. eWeek provided a great article detailing the critical flaw and how the update fixes it. We definitely recommend you read the full article, but the tl:dr is: Bob Rudis, Chief Data Scientist at Rapid7 […]

    Banners from Top 1,000 Ports Now Available to Enterprise Customers

    Over the past year, we spoke with some of our most active customers to determine what other kinds data they would like to see from Censys. The most common request was loud and clear: Scan more ports! Historically, Censys has been known for providing application layer scans of every public IPv4 host across several dozen […]

    How to Find Servers Using MQTT and AMQP Protocols

    Posted on March 19th, 2019 How to Find Servers Using MQTT and AMQP Protocols We recently added MQ Telemetry Transport (MQTT) and the Advanced Message Queuing Protocol (AMQP) protocols to our data set. Here’s a quick rundown of what these protocols are used for, what security risks they carry with them, how to search for […]

    Finding and Securing FTP Sites with Censys

    Finding and Securing FTP Sites with Censys The File Transfer Protocol (FTP) is one of the most popular traditional methods of moving files from one computer to another. While FTP sites are useful for some businesses to send and receive files, for example designs or even customer data, they also quickly become an easy target […]

    Discover SSL/TLS Protocol in Use in Your Organization

    The Internet is built upon its ability to allow devices to communicate with each other and, even back when it was first created, Internet pioneers were thinking about the need for security and privacy. As the Internet continued to grow, the need for “secure” encrypted conversations across the Internet emerged and certain cryptographic standards were […]

    17K Building Control (BACnet) Servers Connected to the Internet

    2200+ Potentially Exposed to High Severity Vulnerability Building Automation and Control network (BACnet) is one of the most popular SCADA protocols that building automation and control systems use to operate. Censys searches for five of the most popular SCADA protocol (including Modbus, S7, BACnet, DNP3, Tridium Fox) and a quick search shows that there are 16,899 BACnet […]

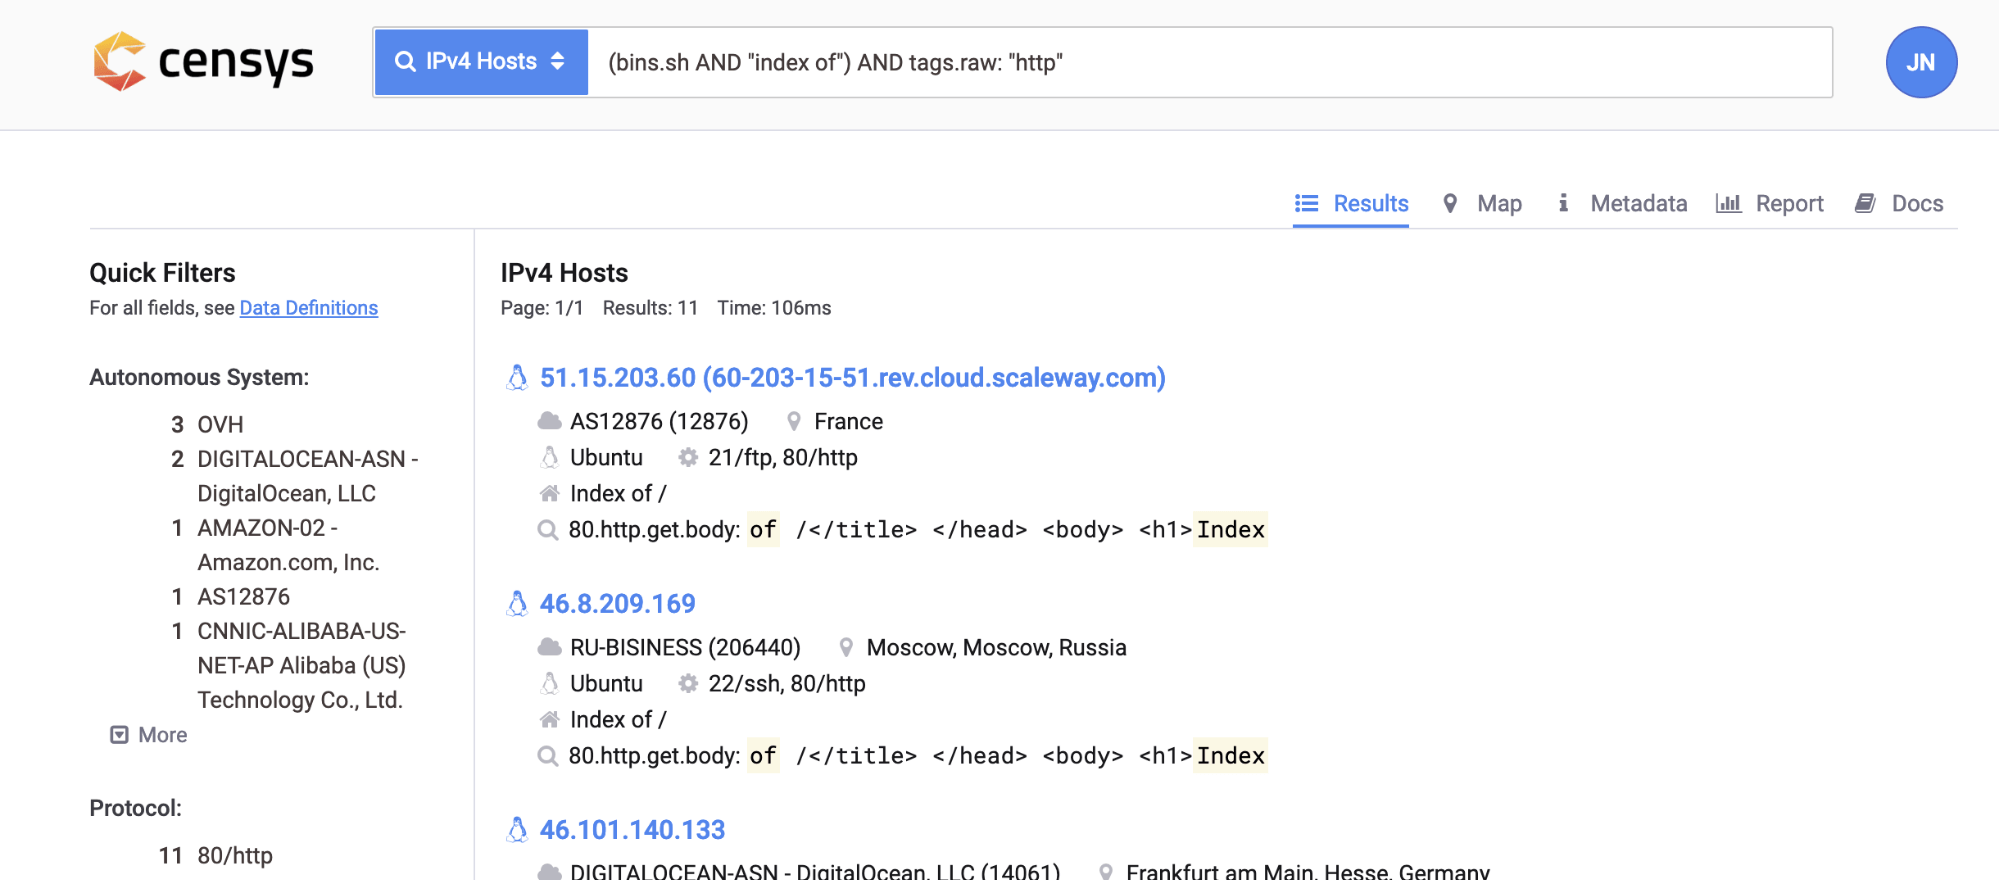
    Hunting Mirai Control Servers Using Known Shell Scripts

    The Mirai Botnet hit the Internet hard in late 2016, infecting hundreds of thousands of Internet of Things (IoT) devices and attacking several high-profile targets with distributed denial-of-service (DDoS) attacks. Effectively, the botnet made several popular sites like AirBnB, Twitter, Github, Reddit, Netflix, and many others inaccessible for most of the East coast, which led […]

    A Dream of the 90s - Bulletin Board Systems

    Do you fondly recall the era where your enthusiasm regarding your Home PC’s modem was met with blank stares or possibly a comment like, “Your computer… has a phone in it?” It was a time before widespread adoption of the Internet, when communities of local Bulletin Board Systems ruled the day in all their ANSI-colored […]