Managing Shadow IT Assets with External Attack Surface Management

    “You can’t protect what you can’t see.” We say this often at Censys because it’s true. Cybersecurity teams can only monitor, manage, and defend the digital assets they know about. Though most enterprise IT teams have protocols in place for proper tech procurement and onboarding, in today’s rapidly expanding cyber landscape, unauthorized digital assets inevitably […]

    Can You Answer These 10 Questions About Your Attack Surface?

    Attack surfaces are top of mind for today’s security leaders, according to the recent Censys 2023 State of Security Leadership report. Surveyed security leaders say that understanding the entirety of the organization’s attack surface is their number one priority for the next 12 months. These leaders know that if they don’t understand all of […]

    Raising the Bar on Internet Coverage: Predictive Scanning Takes The Censys Internet Map to the Next Level

    At Censys, our goal is to be the one place to understand everything on the internet – for more effective threat hunting and exposure management. With the rapid proliferation of cloud providers, software, web properties, remote devices, and more, it is becoming more challenging for security teams to identify threats or exposures and take action. […]

    MikroTik RouterOS CVE-2023-30799: On the Dangers of Public Admin Interfaces

    Continue to track the state of vulnerability with our interactive dashboard Introduction Threat researchers at VulnCheck recently brought renewed attention to a critical remote post-authentication privilege escalation vulnerability in MikroTik RouterOS stable before 6.49.7 and long-term through 6.48.6, tracked as CVE-2023-30799. This exploit was first published by researchers from Margin Research at REcon […]

    Why an Exposure Management Solution Belongs in Your Tech Stack

    Exposure Management solutions are a critical piece of the modern security tech stack. When organizations delay investing in Exposure Management, they limit their ability to effectively defend their security perimeter from attacks. In our recent 2023 State of Security Leadership Report, the majority of surveyed security leaders said that understanding the ENTIRETY of their attack […]

    Mission Critical Intelligence: Why This Government Agency Partners with Censys to Understand the Threat Landscape

    When ZMap, the world’s first global, open-source internet scanner, was released in 2012, it immediately attracted tens of thousands of users from leading government agencies who conducted critical searches to understand the emerging digital threat landscape. Today, Censys’ proprietary Internet Map is the most comprehensive, up-to-date collection of global internet infrastructure enriched with critical context […]

    Managed File Transfer (MFT) Exposure

    Attackers Targeting MFT Tools Are On The Rise There is a constant war of convenience vs security being waged and moving files across networks is one of those battles being fought right now. While many of these tools are designed to only be accessed behind a firewall, they are often incorrectly configured to be accessed […]

    Identifying CISA BOD 23-02 Internet-Exposed Networked Management Interfaces with Censys

    UPDATE 2023-06-28: A section of the second paragraph of this article describing the FCEB hosts we examined for this analysis was edited for clarity. Executive Summary On June 13, CISA released BOD 23-02 with the objective of mitigating the risks associated with remotely accessible management interfaces that might allow configuration or control of federal agency […]

    Latest CISA Directive Highlights Importance of Attack Surface Visibility

    Latest CISA Directive Highlights Importance of Attack Surface Visibility By Brad Brooks, Chief Executive Officer, Censys Earlier this week, the Cybersecurity and Infrastructure Security Agency (CISA) issued a new binding operational directive (BOD) requiring federal civilian agencies to enhance protections for devices on government information systems that use network protocols for remote management over public […]

    MOVEit: an Industry Analysis

    Note: As Censys is an internet scanner, we cannot determine if these devices are vulnerable; these are the MOVEit services we found running exposed on the internet.  Introduction Recently, Managed File Transfer (MFT) services have been gaining considerable attention in the realm of security. Although MFT may not be a regular discussion topic, it is […]

    MOVEit Transfer Vulnerability

    UPDATES: SUMMARY: Another day, another MFT (Managed File Transfer) product getting pwned. On the heels of the GoAnywhere MFT 0-day, this time, it’s a vendor called Progress Software Corporation and their product, “MOVEit Transfer,” that facilitates the transfer of files between business partners and their customers using a variety of protocols such as SSH and […]

    Zyxel Vulnerabilities

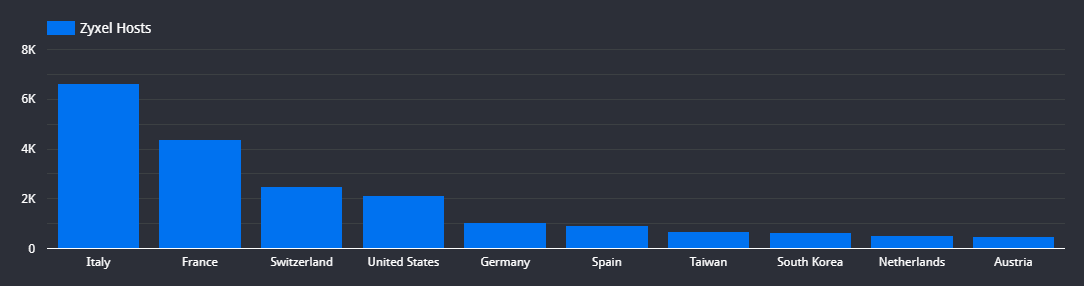
    Zyxel has had an interesting run the last few weeks, with three new vulnerabilities: CVE-2023-33009, CVE-2023-33010, and the most critical, CVE-2023-28771. The Mirai botnet is currently exploiting CVE-2023-28771. Censys found 24,457 potentially vulnerable Zyxel ATP, USG, and VPN products exposed to the internet. 86.72% of these hosts run the IKE protocol required for successful CVE-2023-28771 […]

    Internet Footprint of SOHO Devices Exploited by Volt Typhoon

    On May 24, 2023, Microsoft announced that they’d discovered “stealthy and targeted malicious activity” focused on communications critical infrastructure of the US and Guam. The attacks are attributed to a Chinese state-sponsored actor dubbed Volt Typhoon, who has been active since mid-2021. One of Volt Typhoon’s primary techniques is living off the land, which […]

    Months after first GoAnywhere MFT zero-day attacks, Censys still sees ~180 public admin panels

    GoAnywhere MFT Breaches by high-profile ransomware groups have now affected 8 confirmed organizations (and counting) Executive Summary: Timeline: The Internet’s Response: We observe a slow and steady patch response to this actively exploited vulnerability. Since this zero-day was first disclosed, Censys has seen an approximate 46% decrease in the number of exposed GoAnywhere Admin Panels […]

    Total Economic Impact™: Censys EASM Customer Voices

    Who better to talk about the value of a solution than the folks who actually use it? As part of the recent Total Economic Impact of Censys External Attack Surface Management study, Forrester Consulting independently interviewed Censys customers to learn more about the business value they achieve with our Censys EASM solution. The big […]

    Virtual Ghosts

    These servers should not exist! Now Generally Available for all Censys customers is a new asset type, Web Entities. A “Web Entity” in Censys allows users to treat their web-based assets as a single high-level commodity, grouping hosts and services as part of an organization’s web service ecosystem. In addition to introducing this new data […]

    Revolutionize Network Reconnaissance with AI-Powered CensysGPT: Simplify Queries & Enhance Security

    At Censys we pride ourselves on being innovators and encourage creativity, experimentation and collaboration amongst our team. During our 2023 Hackathon, we challenged our engineering team to develop ideas for new solutions that would improve our customer experience and make our product more accessible. Our integrations team rose to the challenge with an exciting […]

    Total Economic Impact™ : How Does Censys EASM Deliver Value to Customers?

    Censys recently commissioned Forrester Consulting to conduct an independent study of the Total Economic Impact™ of the Censys External Attack Surface Management (EASM) solution. Learn more about what the study found and how to access your copy.  When you’re weighing the pros and cons of adding a new solution to your security tech stack, understanding […]