5 Ways to Win Buy-In for Better Internet Intelligence

    Internet intelligence is at the heart of any successful cybersecurity strategy. Whether you’re proactively searching for suspicious activity or reacting to a CVE that just dropped, you can’t do your job well without if you don’t have a full view into today’s evolving threat landscape. However, sometimes security teams and stakeholders within the organization aren’t […]
    Four Oh Four: A Look at Our Favorite Status Code

    Happy 404 day from Censys! Here are some fun stats involving our favorite “resource not found” HTTP status code! We’ve all experienced it: you’re leisurely browsing the web, surfing along, and suddenly come across this: 404 Page Not Found. When a user encounters a 404 error, it could mean that the user incorrectly entered the […]

    Spotlight: Women & Innovation at Censys

    Women drive innovation across all areas at Censys, from engineering and product design, to research, marketing, and beyond. In celebration of Women’s History Month and our ongoing commitment to gender equality, we recently spoke with some of our incredible teammates about their work. Himaja Motheram | Security Researcher  What kinds of projects do you work […]

    Before the Ink Dries: Assessing M&A Cyber Risk

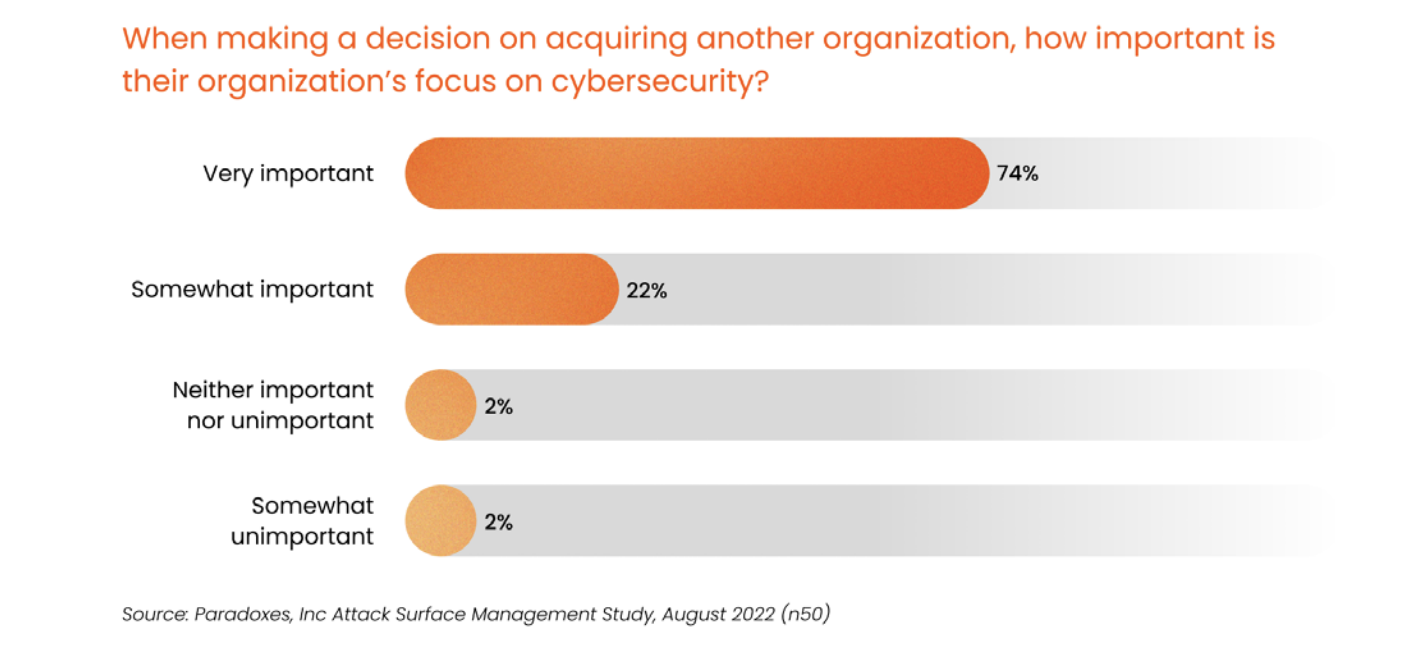
    Mergers and acquisitions may be common, but they’re not without risk, especially when it comes to cybersecurity risk. As cyberattacks increase in frequency and sophistication, the last thing any parent company wants to discover is that they’ve inherited mismanaged or unmanaged assets. Yet, assessing the scope of potential risk can be a tall order. An […]

    4 Cybersecurity Webinars Worth Your Watch

    Haven’t had a chance to tune in to some of our recent webinars? Catch up on what you’ve missed with these on-demand recordings! You can stream the recordings at any time from the links below. Profiles in Threat Hunting: Finding Threats by Observing Behaviors Presenters: Censys Senior Security Researcher Emily Austin; Censys Director of Federal […]

    Potential Chinese Influence on African IT Infrastructure

    Between 10-21 February 2023, Censys discovered over 46,000 commercial devices associated with four U.S. blacklisted Chinese tech manufacturers in Kenya, Zambia, South Africa, and Mauritius. Huawei, ZTE, Hikvision, and Dahua were blacklisted by the U.S. government in November of 2022 and the importation or sale of their equipment was banned in the U.S. […]

    What You Need to Know About Biden's Long Awaited Cybersecurity Strategy

    The Biden Administration’s long awaited National Cybersecurity Strategy was released outlining the strategy, goals, and implementation plan to drive a robust, collaborative approach to securing our global digital landscape. To mitigate the ever-mounting risk in both the public and private sectors, The White House places cybersecurity as a central tenant to the functioning of […]

    ESXiArgs: History, Variants, and SLP!

    Last week, we discovered two potential early victims of ESXiArgs (Host-A, Host-B) after noticing that they were the only two hosts with the ransom note on February 1 and January 31, 2023. Manually searching our data, we determined that they’d had a variant of the ransom note since mid-October 2022, but we were […]

    Unlocking the Potential of X.509 Certificate Data

    We are celebrating the launch of Certs 2.0 – the largest X.509 certificate repository in existence! ???? Our new Certs 2.0 index provides enhanced access to our extensive billion certificate repository, with more efficient and granular searching capabilities. Additional benefits include: With all these new goodies available, we wanted to take a moment and review why […]

    Why This European Government Agency Uses Attack Surface Management

    Attack surface management (ASM) is becoming an integral, value-add strategy for cybersecurity teams across industries, including those in government. Our own partnerships with government agencies around the world highlight how ASM complements government threat hunting and response efforts. Teams use ASM tools like the Censys Attack Surface Management Platform to gain greater visibility into […]

    RCE Zero Day in GoAnywhere MFT [CVE-2023-0669]

    The list of organizations who have come forward as victims of a GoAnywhere breach has grown long: Community Health Systems, Hatch Bank, Hitachi Energy, Rubrik, the City of Toronto, Procter & Gamble, Saks Fifth Avenue, and Crown Resorts. update 2023-03-17 Hitachi Energy has become the 3rd organization to report a data breach in its GoAnywhere […]

    The Evolution of ESXiArgs Ransomware

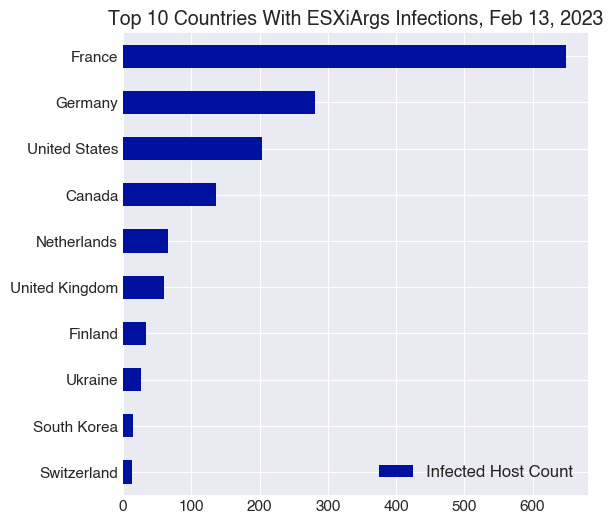
    Mark Ellzey & Emily Austin Please see our new post, ESXiArgs: History, Variants, and SLP! for the latest updates. Executive Summary Over the last few days, Censys has observed just over 500 hosts newly infected with ESXiArgs ransomware, most of which are in France, Germany, the Netherlands, and the UK. During analysis, we discovered two […]

    Follow-up on Russian “Host F”

    (As reported in “Russian Ransomware C2 Network Discovered in Censys Data”) Executive summary In late January 2023 Censys analysts reviewed Host F (95.213.145.99), which was previously identified in Censys reporting as a Russia-based, probably malicious host running a Command and Control (C2) ransomware kit with callbacks to an associated Bitcoin wallet. Upon return to the […]

    This Week's Top Three Trends in Cybersecurity

    The Censys research team has been tracking some of this year’s most significant vulnerabilities, and making headlines with their work in the process. Read more about three of the vulnerabilities the team has tracked using our internet intelligence data and find the latest on where things stand with each vulnerability’s risk remediation. ESXiArgs ransomware […]

    ESXWhy: A Look at ESXiArgs Ransomware

    Emily Austin & Mark Ellzey UPDATE 2023-02-15 Please see our new post, The Evolution of ESXiArgs Ransomware, for further updates. UPDATE 2023-02-13 Over the weekend (2023-02-09 through 2023-02-11), we’ve seen a slight increase in the number of infected hosts, where at the time of writing, there were 1,994 hosts found in our search engine. We […]

    6 Steps Threat Profilers Can Follow to Uncover Ransomware (and Other Nefarious Activity)

    Ransomware attacks have dominated headlines in recent years, as attackers take aim at an increasing variety of targets, from school districts to critical infrastructure networks. Ransomware accounted for 25% of all breaches in 2022, according to the Verizon Data Breach Investigations Report, and in early 2022, CISA reported that it had observed incidents of ransomware […]

    Responding to the Lowering Cost of Cyber Hostility

    As cyber hostility increases in volume, it’s easy to forget that the increases span the spectrum of sophistication. Zero day exploits and multi-million dollar ransoms might grab headlines, but the cost and ease of executing simple attacks is only getting cheaper and more accessible. Therefore, the digital security threats prevented by basic hygiene and sound […]