Why Did a Cybersecurity Company Choose Censys Data Over Competitors?

    We know that fresh, accurate, and timely data is the key ingredient to any cybersecurity intel effort. Security teams can have all the tools and manpower in the world, but without access to the right data (the kind of data that also reduces false positives and minimizes noise) security efforts will ultimately fall short. […]
    Tracking a SugarCRM Zero-Day

    Update January 17th, 2023: SugarCRM had a third-party forensics firm validate that there was no intrusion to their cloud-based products due to this vulnerability. More information on that can be found here. Update January 11th, 2023: This issue is now being tracked as CVE-2023-22952 / Updated compromised tallies Update January 10th, 2023: SugarCRM is aware of […]

    Using Censys to Find Misconfigured S3

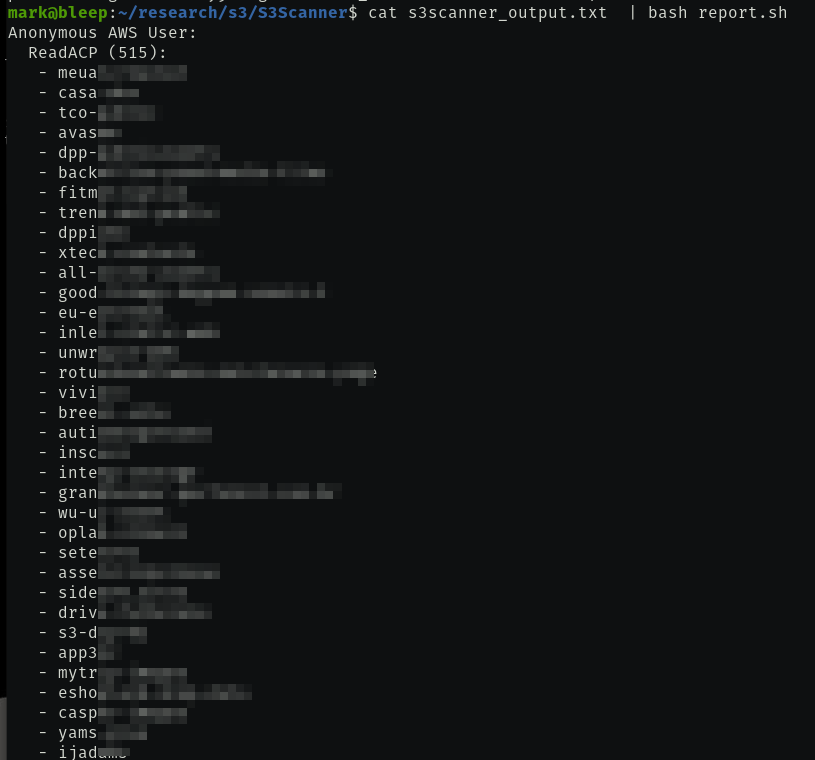
    Findings In under an hour using Censys data, we found 7,640 potential S3 buckets, 49 completely open (World Read + Write), 16 buckets with anonymous write, 1,235 with anonymous read access, and more. Finding S3 Targets With Censys Amazon S3 (Amazon Simple Storage Service) is a product that provides object storage over the web […]

    How a State Agency Automated Attack Surface Management in the Age of Remote Work

    Soon after the Covid-19 pandemic hit, Censys partnered with a state agency that wanted to scale their risk management program by automating attack surface discovery and tracking. New challenges had emerged after their workforce moved to a remote working state. Key benefits By partnering with Censys, the state agency gained: The goals Manage attack surface […]

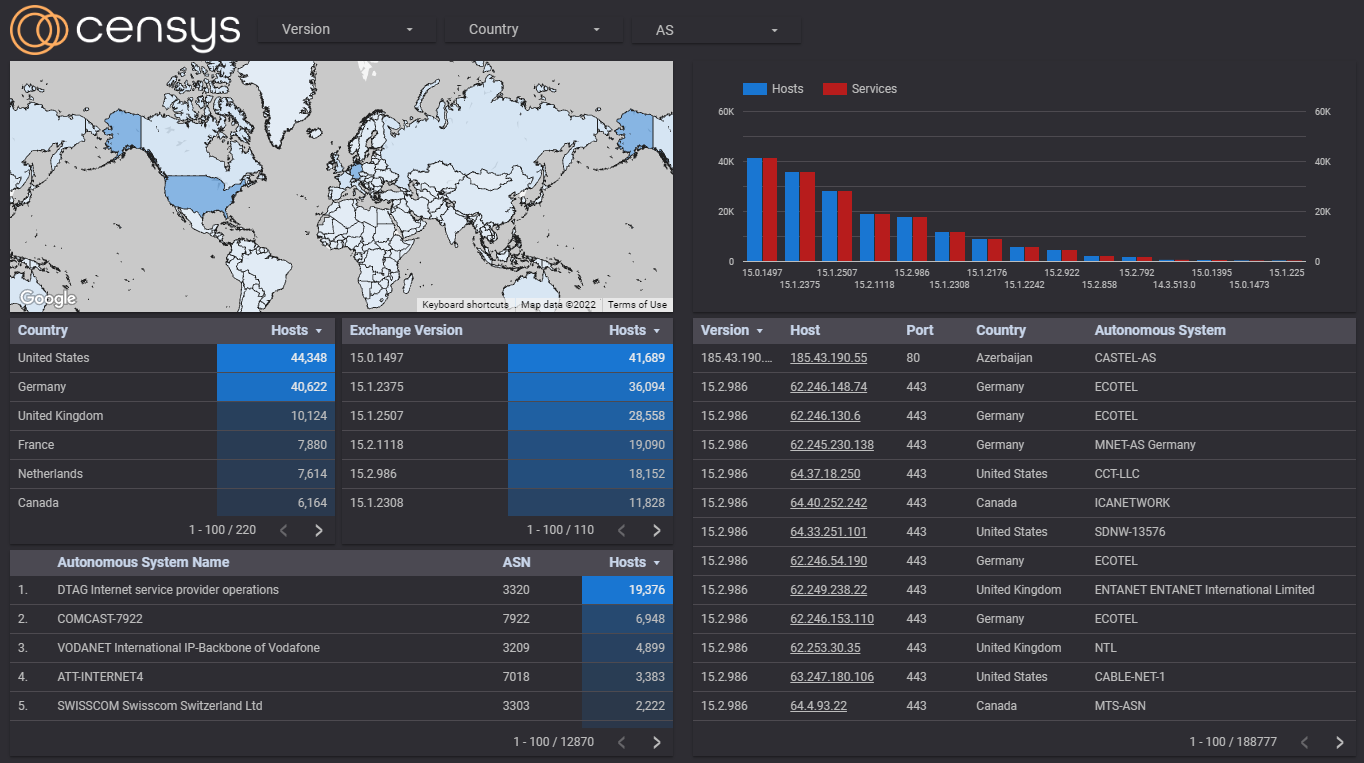
    Pulse Connect Secure: A View from the Internet

    Pulse Connect Secure is a low-cost and widely-deployed SSL VPN solution for remote and mobile users. Over the years, researchers have found several significant vulnerabilities in the server software, some even resulting in the active exploitation of critical infrastructure by malicious threat actors. In April of 2021, CISA released a report detailing some of […]

    Critical Vulnerability (CVE-2021-35587) in Oracle Fusion Middleware Now Exploited!

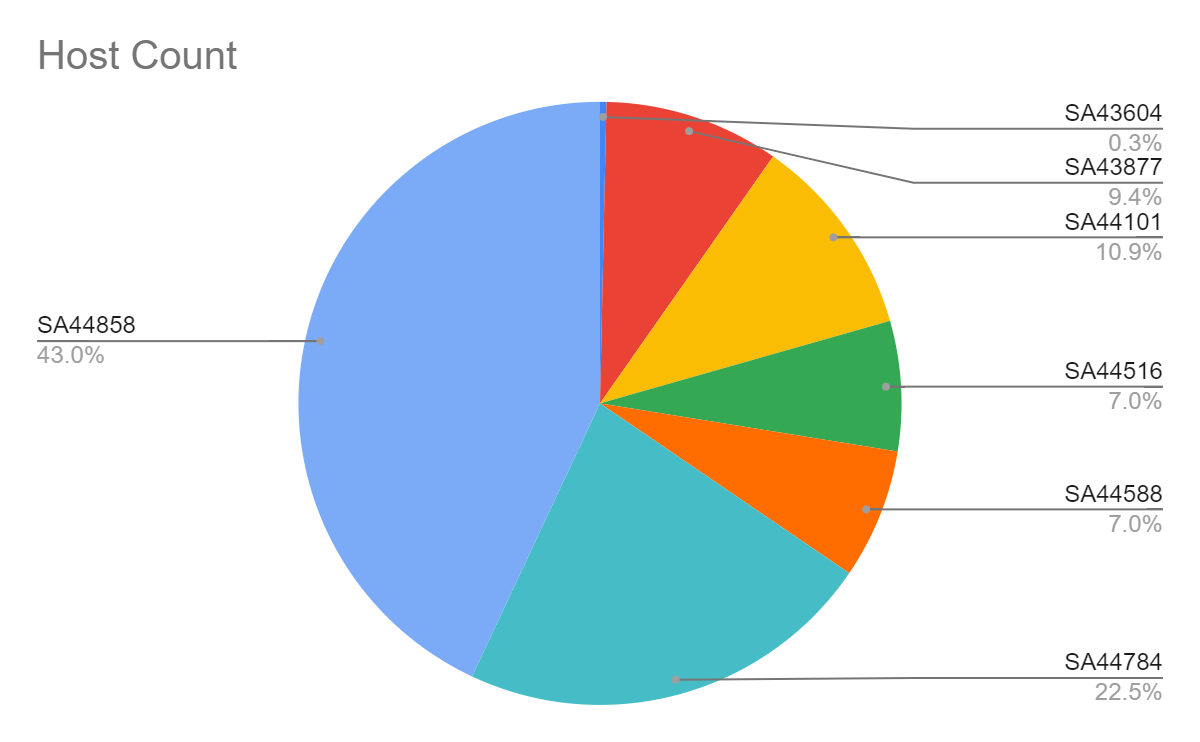
    On Monday, November 28, 2022, the Cybersecurity & Infrastructure Security Agency (CISA) added CVE-2021-35587 and CVE-2022-4135 to its Known Exploited Vulnerabilities Catalog and provided an update based on evidence of active exploitation. CVE-2021-35587 is associated with Oracle Fusion Middleware Access Management, which is an enterprise level Single Sign-on (SSO) solution.  CVE-2021-35587 allows for Pre-auth Remote Code […]

    ProxyNotShell Proof Of Concept Now Public

    Last week, a security researcher known as “Janggggg” published a proof of concept (PoC) exploit for the latest “ProxyNotShell” vulnerabilities in Microsoft Exchange that were discovered in September. ProxyNotShell is already confirmed to be actively exploited by a Chinese nation-state threat actor at the time of the vulnerability announcement by Microsoft. The attack was initially […]

    Here's How Citizen Lab Used Censys to Expose a Spyware Vendor

    The Challenge: Spyware from Candiru was used to impersonate sites from well-known advocacy organizations to target activists and human rights workers. Citizen Lab, a research institute at the University of Toronto, used Censys data to understand impersonated sites, passing the details forward to Microsoft Threat Intelligence Center (MSTIC) to find exploits. What Citizen Lab achieved […]

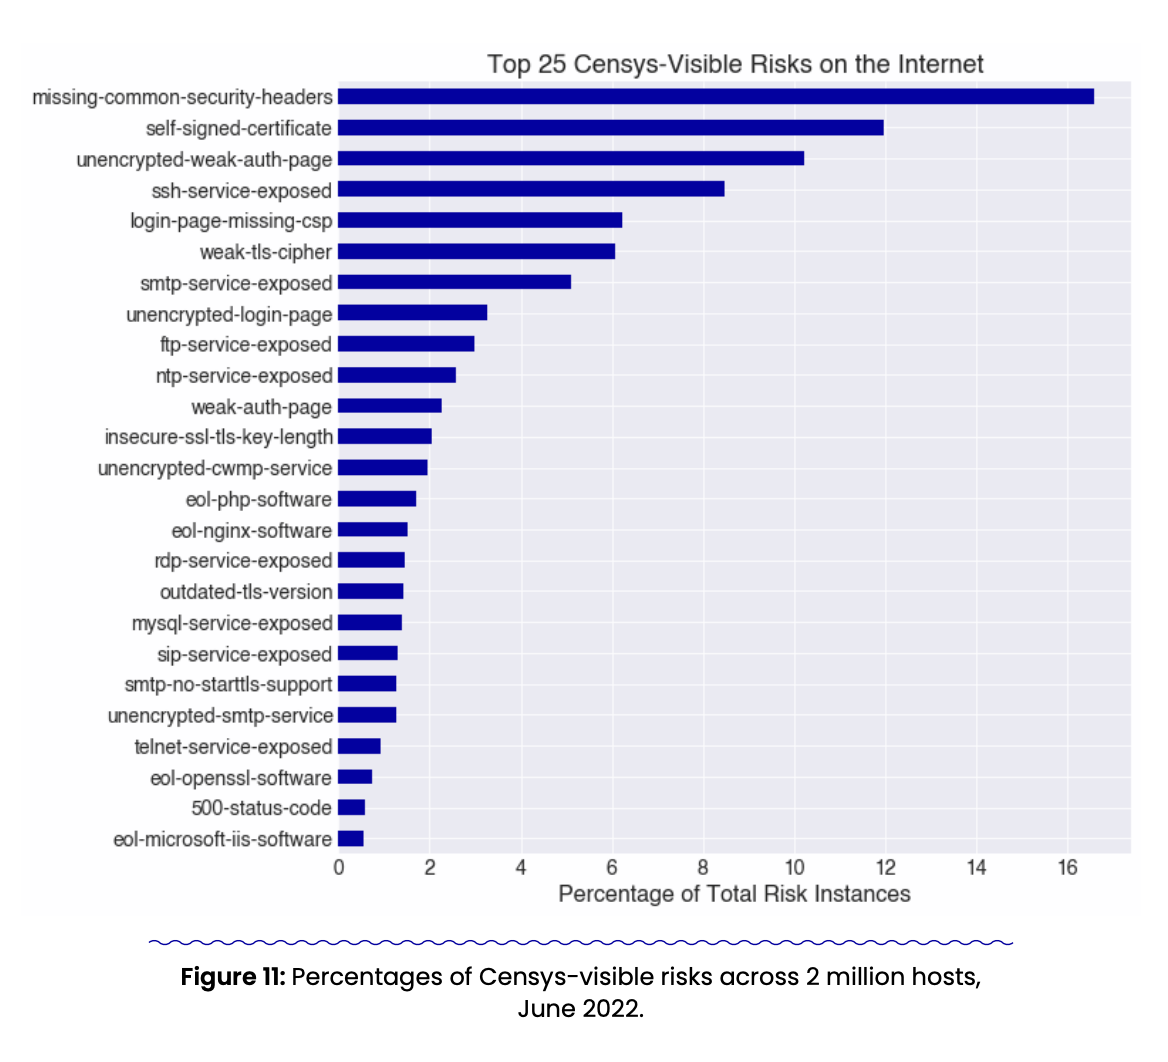
    A Closer Look: Risks in Finance

    As part of our State of the Internet Report blog series, we’re taking a closer look at findings from an industry perspective. Specifically, which risks were most commonly observed among sampled Finance and Insurance organizations? It goes without saying that maintaining good cybersecurity hygiene in the finance and insurance space is paramount– these organizations […]

    Critical Vulnerability in OpenSSL!

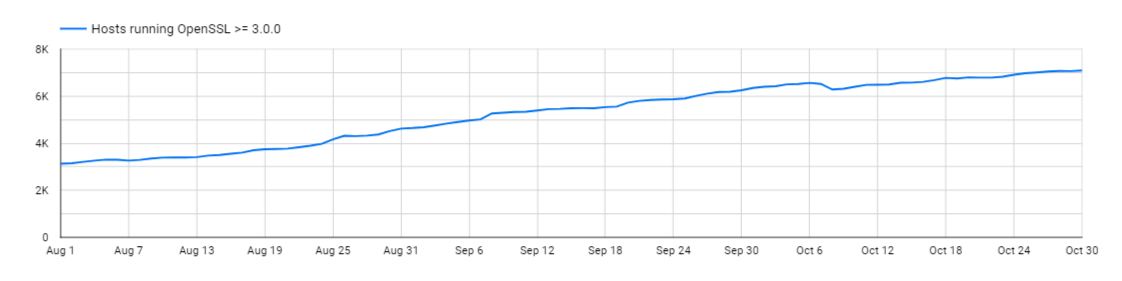
    Quick Links Censys Search Query for OpenSSL >=3.0.0 Censys ASM Inventory Query for OpenSSL >= 3.0.0 OpenSSL vendor vulnerability announcement. **Updates** 2022-11-01 Details of two high-severity vulnerabilities patched in OpenSSL version 3.0.7 are now available (CVE-2022-3786, CVE-2022-3602). Both are buffer overflows in the X.509 certificate verification process, “specifically in name constraint checking.”  The first, CVE-2022-3786, […]

    Who's Down with IPP? Finding Internet-Connected Printers with Censys

    In the Internet of Things (IoT) arena, printers might seem like the least of our problems. We’ve got new smart home devices connecting to the Internet every day—refrigerators, home security systems, washing machines (spoiler alert, your clothes are now clean and, no, you probably don’t need an app to know that). Arguably more worrisome are […]

    Understanding the Attack Surface of the Internet

    In part-two of our Threat Detection, Defense & Remediation Using ASM series – based on this recent eBook from the Censys Research Team – we’re exploring the attack surface of the Internet. How is it evolving, and what do changes in the Internet’s attack surface mean for corporate cybersecurity? When we talk about the “attack […]

    How Swiss Life Gained Efficiency & Improved Workflow with Censys

    As a financial company that deals in a critical aspect of their clients’ lives, Swiss Life attaches great importance to their corporate governance policies. In following with their procedures around international accounting, auditing, and a code of conduct to safeguard the interests of their shareholders, policyholders, and staff, Swiss Life wanted to better understand […]

    GreyNoise Research Finds Censys Scan Data Is Fastest, Most Comprehensive

    Cybersecurity firm GreyNoise Intelligence recently published “A Week In the Life of a GreyNoise Censor: A Benign View.” I’m incredibly excited about this blog because anytime an organization outside of yours conducts research that reinforces statements you make on a daily basis, it’s a wonderful thing. There’s even still some additional nuance to be explored, […]

    In Support of the New CISA Directive (What It Means & How to Take Action)

    Earlier this month, the federal government’s Cybersecurity and Infrastructure Security Agency (CISA) issued Binding Operational Directive 23-01: Improving Asset Visibility and Vulnerability Detection on Federal Networks. The directive applies to all Federal Civilian Executive Branch systems and the agencies operating those systems. CISA states that their directive is an effort to make more measurable progress […]