Tracking AyySSHush: a Newly Discovered ASUS Router Botnet Campaign
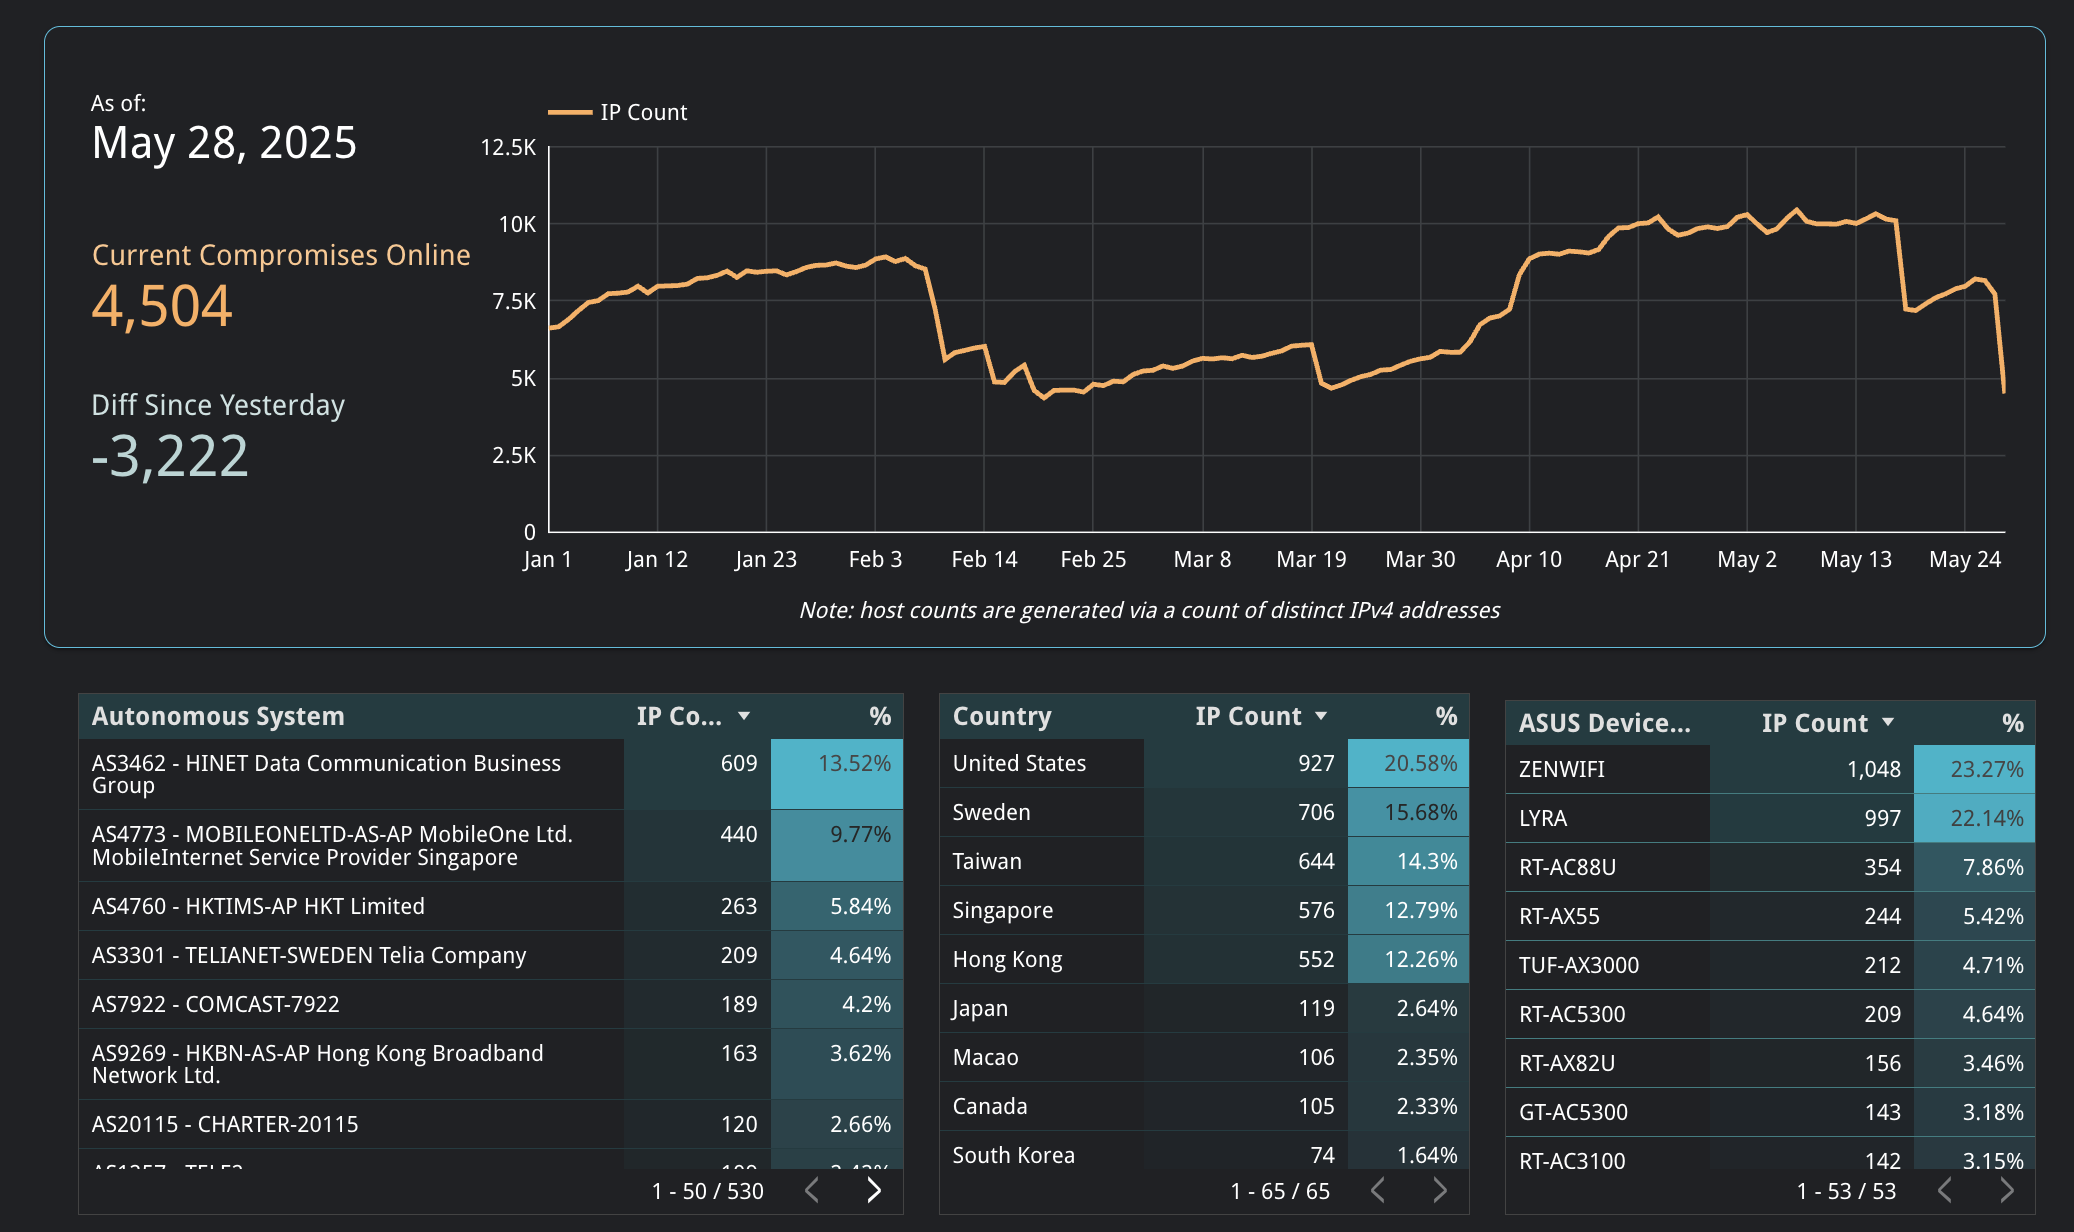
Discover AyySSHush, a stealthy ASUS router botnet compromising 4,500+ devices globally. Learn how it abuses firmware features to persist across resets and evade detection.
Discover AyySSHush, a stealthy ASUS router botnet compromising 4,500+ devices globally. Learn how it abuses firmware features to persist across resets and evade detection.
Uncovering hidden IOCs behind TikTok malware campaigns using AI-generated videos. Deep dive into Vidar & StealC info-stealers, malicious domains & PowerShell scripts.
Censys outperforms Shodan, ZoomEye & other scanning engines with 92% accuracy, 82% port coverage, and 10x faster data updates. See the full research comparison.
Discover how the Censys Threat Hunting Module empowers government teams to detect adversary infrastructure before attacks. Proactive threat intelligence for national security.
Censys Risk Evidence cuts alert triage time by explaining why risks fired with clear, linked scan data. Reduce false positives and accelerate threat detection in your SOC.
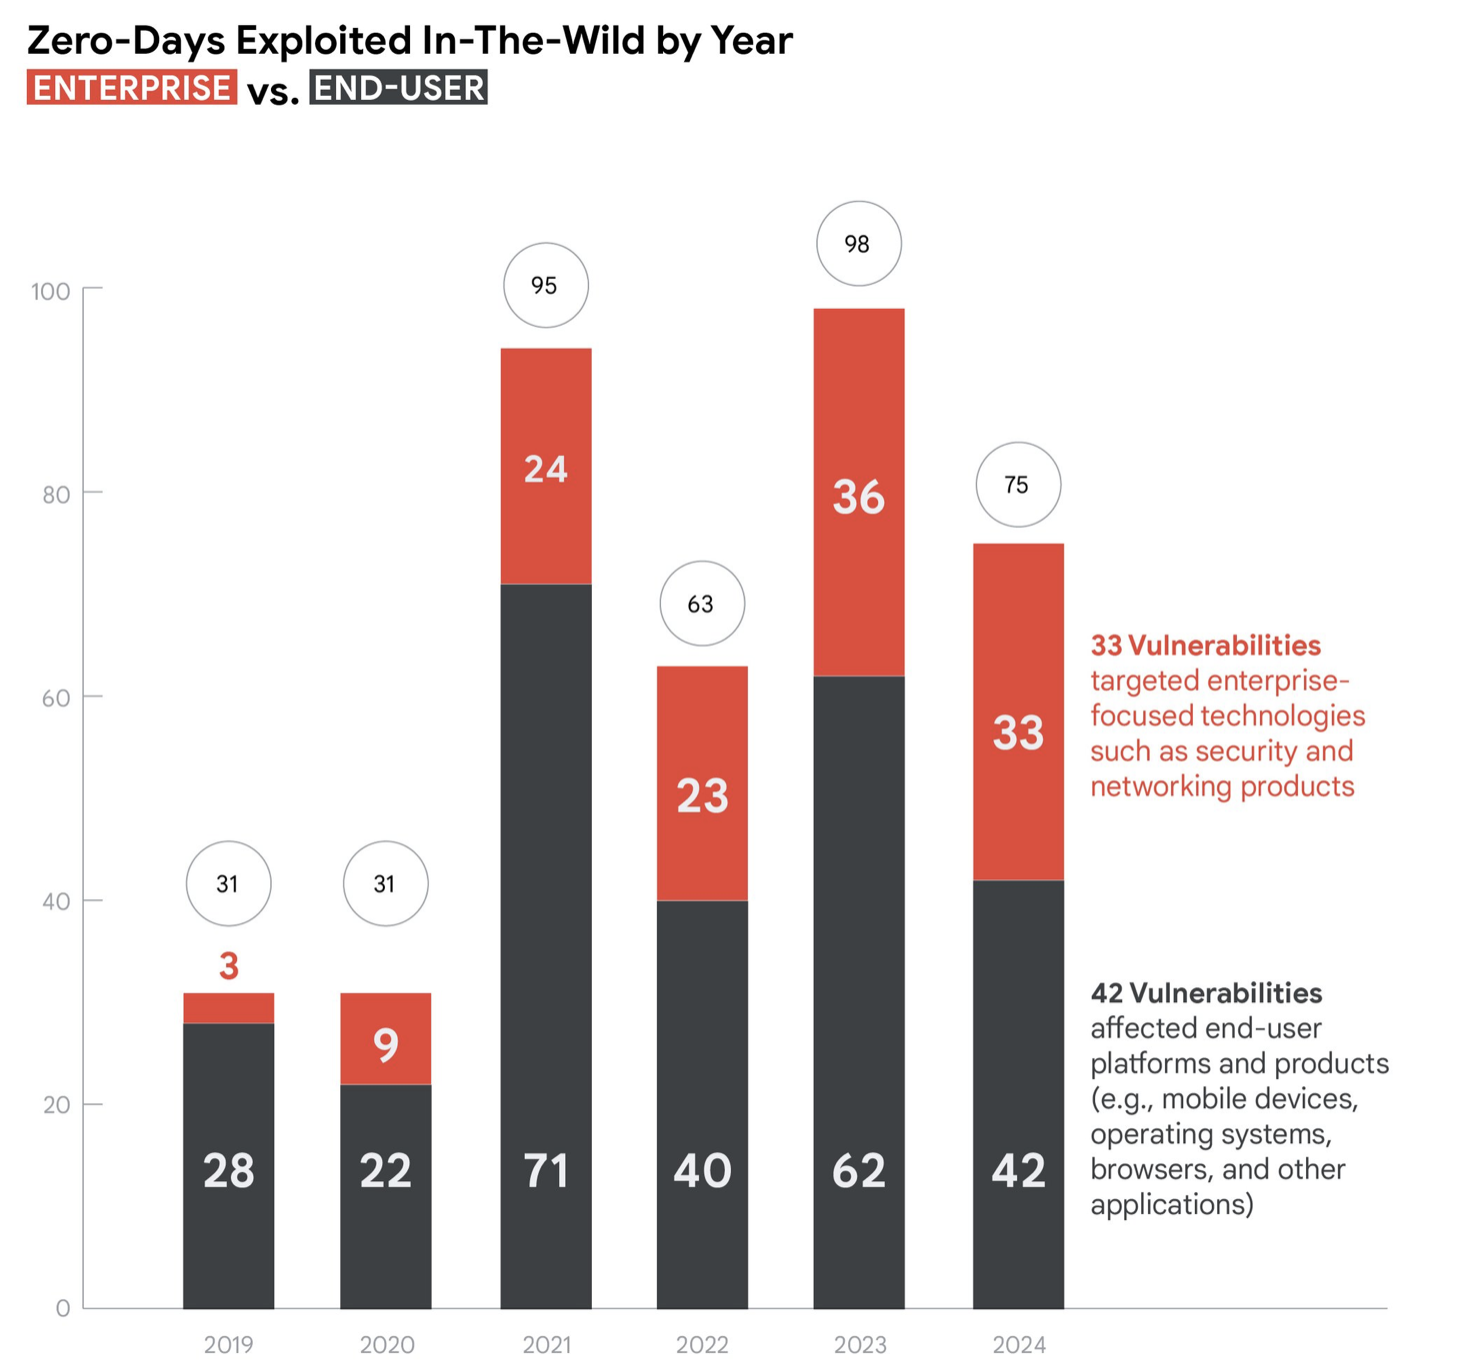
Google data reveals 2024 zero-day trends: 75 vulnerabilities found, with 44% targeting enterprise security and networking products. Learn which vendors are most at risk.
**Discover exposed ports & protocols with Censys ASM's new dashboard. Gain real-time attack surface visibility across all 65K+ ports to find hidden risks and misconfigurations fast.**
CISA's BOD 25-01 mandates secure cloud practices for federal agencies. Learn how SCuBA baselines and cloud security hygiene defend against evolving threats.
"Discover the Censys Query Assistant: search the internet using natural language in any language. Simplify threat hunting & attack surface management—no syntax needed."
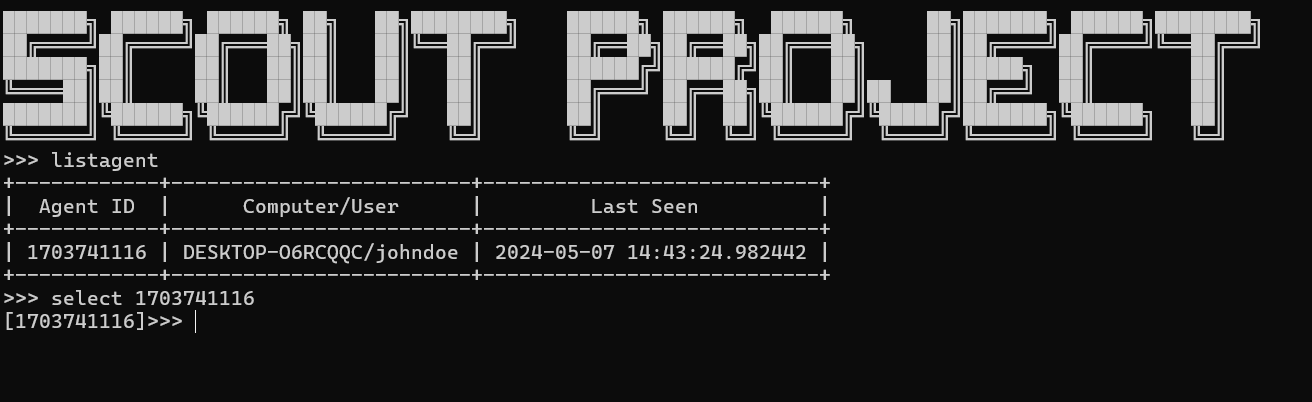
Censys uncovers "SCOUT PROJECT," a novel C2 server exploiting CVE-2025-30208, CVE-2025-3248 & CVE-2025-29927. Discover the threat actor's infrastructure, backdoor toolkit, and attack methods.
Reduce defender dwell time with Censys Threat Module. Hunt adversary infrastructure faster, enrich threat intel with MITRE & Malpedia, and act before threats mature.
Track Salt Typhoon's attack surface: Censys research reveals 6-month exposure trends for Cisco, Sophos, Ivanti & Fortinet devices targeted by this Chinese state-sponsored threat actor.
Discover how Censys delivers timely, context-rich threat intelligence on adversary infrastructure. Move beyond stale IPs with actionable IOCs, Actor Profiles & more.
Edge device vulnerabilities surged in 2024, driving a 34% increase in breach exploitation. Verizon DBIR reveals growing attack surface management challenges for defenders.
Discover how Censys uses CursorAI and GreyNoise data to hunt adversary infrastructure like ORB networks. Learn to identify malicious SOCKS proxies in residential networks.
CISA extends MITRE's CVE program contract after funding scare. Learn how the near-lapse exposed fragilities in the vulnerability management system the security industry depends on.
Chinese Volt Typhoon & Salt Typhoon cyber espionage campaigns expose critical infrastructure weaknesses. Learn how adversary infrastructure threats demand advanced threat hunting.
Discover how the Lucid phishing-as-a-service platform powers massive SMS toll scam campaigns using device farms, thousands of domains, and infrastructure traced to China.
Around 5,000 hosts expose Kubernetes NGINX ingress controllers to the internet. Censys researchers analyze the critical RCE vulnerability and its real-world impact.
**Censys ARC Research Team uncovers RedPenguin malware targeting Juniper MX routers with advanced C2 techniques, UDP backdoors & Tiny SHell. Learn how attackers evade detection.**